Proof-based DAST
Know which vulnerabilities
are really exploitable.
Stop triaging false positives and fix what attackers can actually reach.
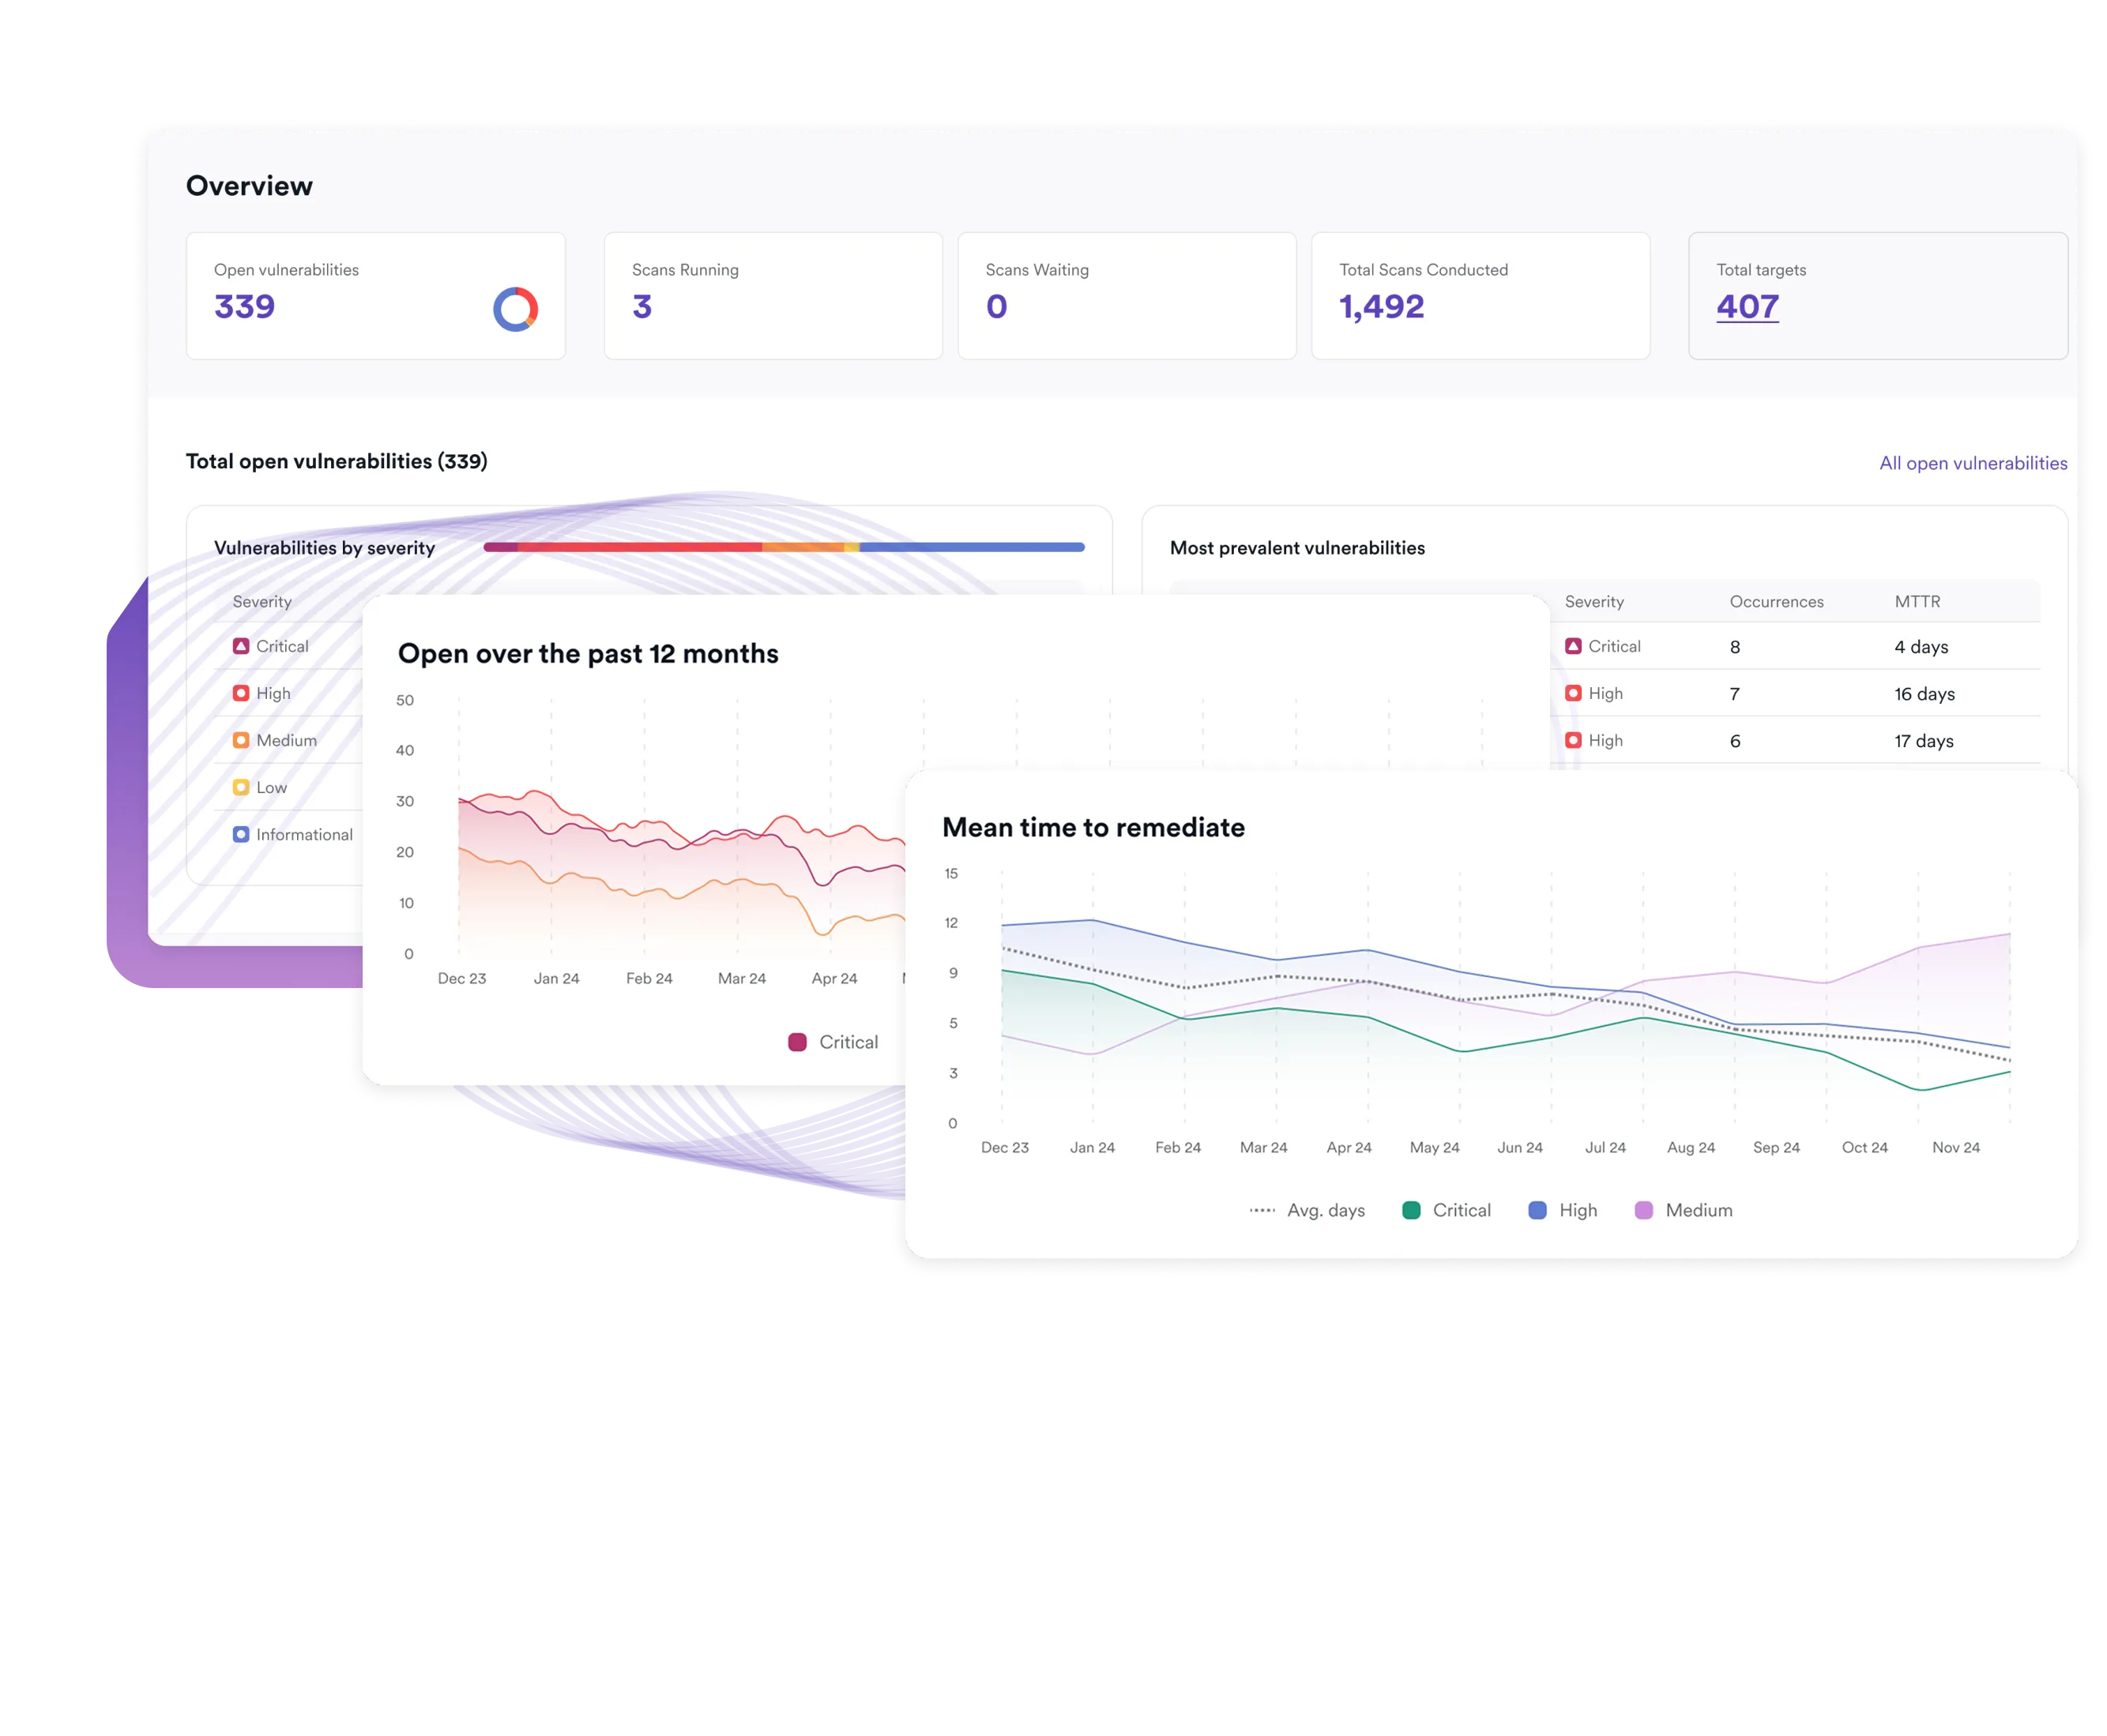
- Proof of exploit: Every confirmed finding comes with evidence, so developers trust the report.
- Web apps and APIs: One scanner for the front end, the back end and every API in between.
- Built for CI/CD: Trigger scans from your pipeline and sync results to the tools your teams already use.
Book a DAST demo
5000+ Top Organizations Trust Invicti


Why scanner reports get ignored
Three problems turn security findings into noise instead of fixes.

Too many false alarms
Developers learn to distrust a scanner that is wrong half the time.

Slow feedback
Findings that arrive weeks after the commit are expensive to fix.

No proof
Without evidence of exploitability, every ticket becomes a debate.
Evidence, not guesses
Proof-based scanning safely exploits each finding and records the result, so only confirmed vulnerabilities reach your backlog
Talk to an expertAccuracy
Fewer tickets, all of them real
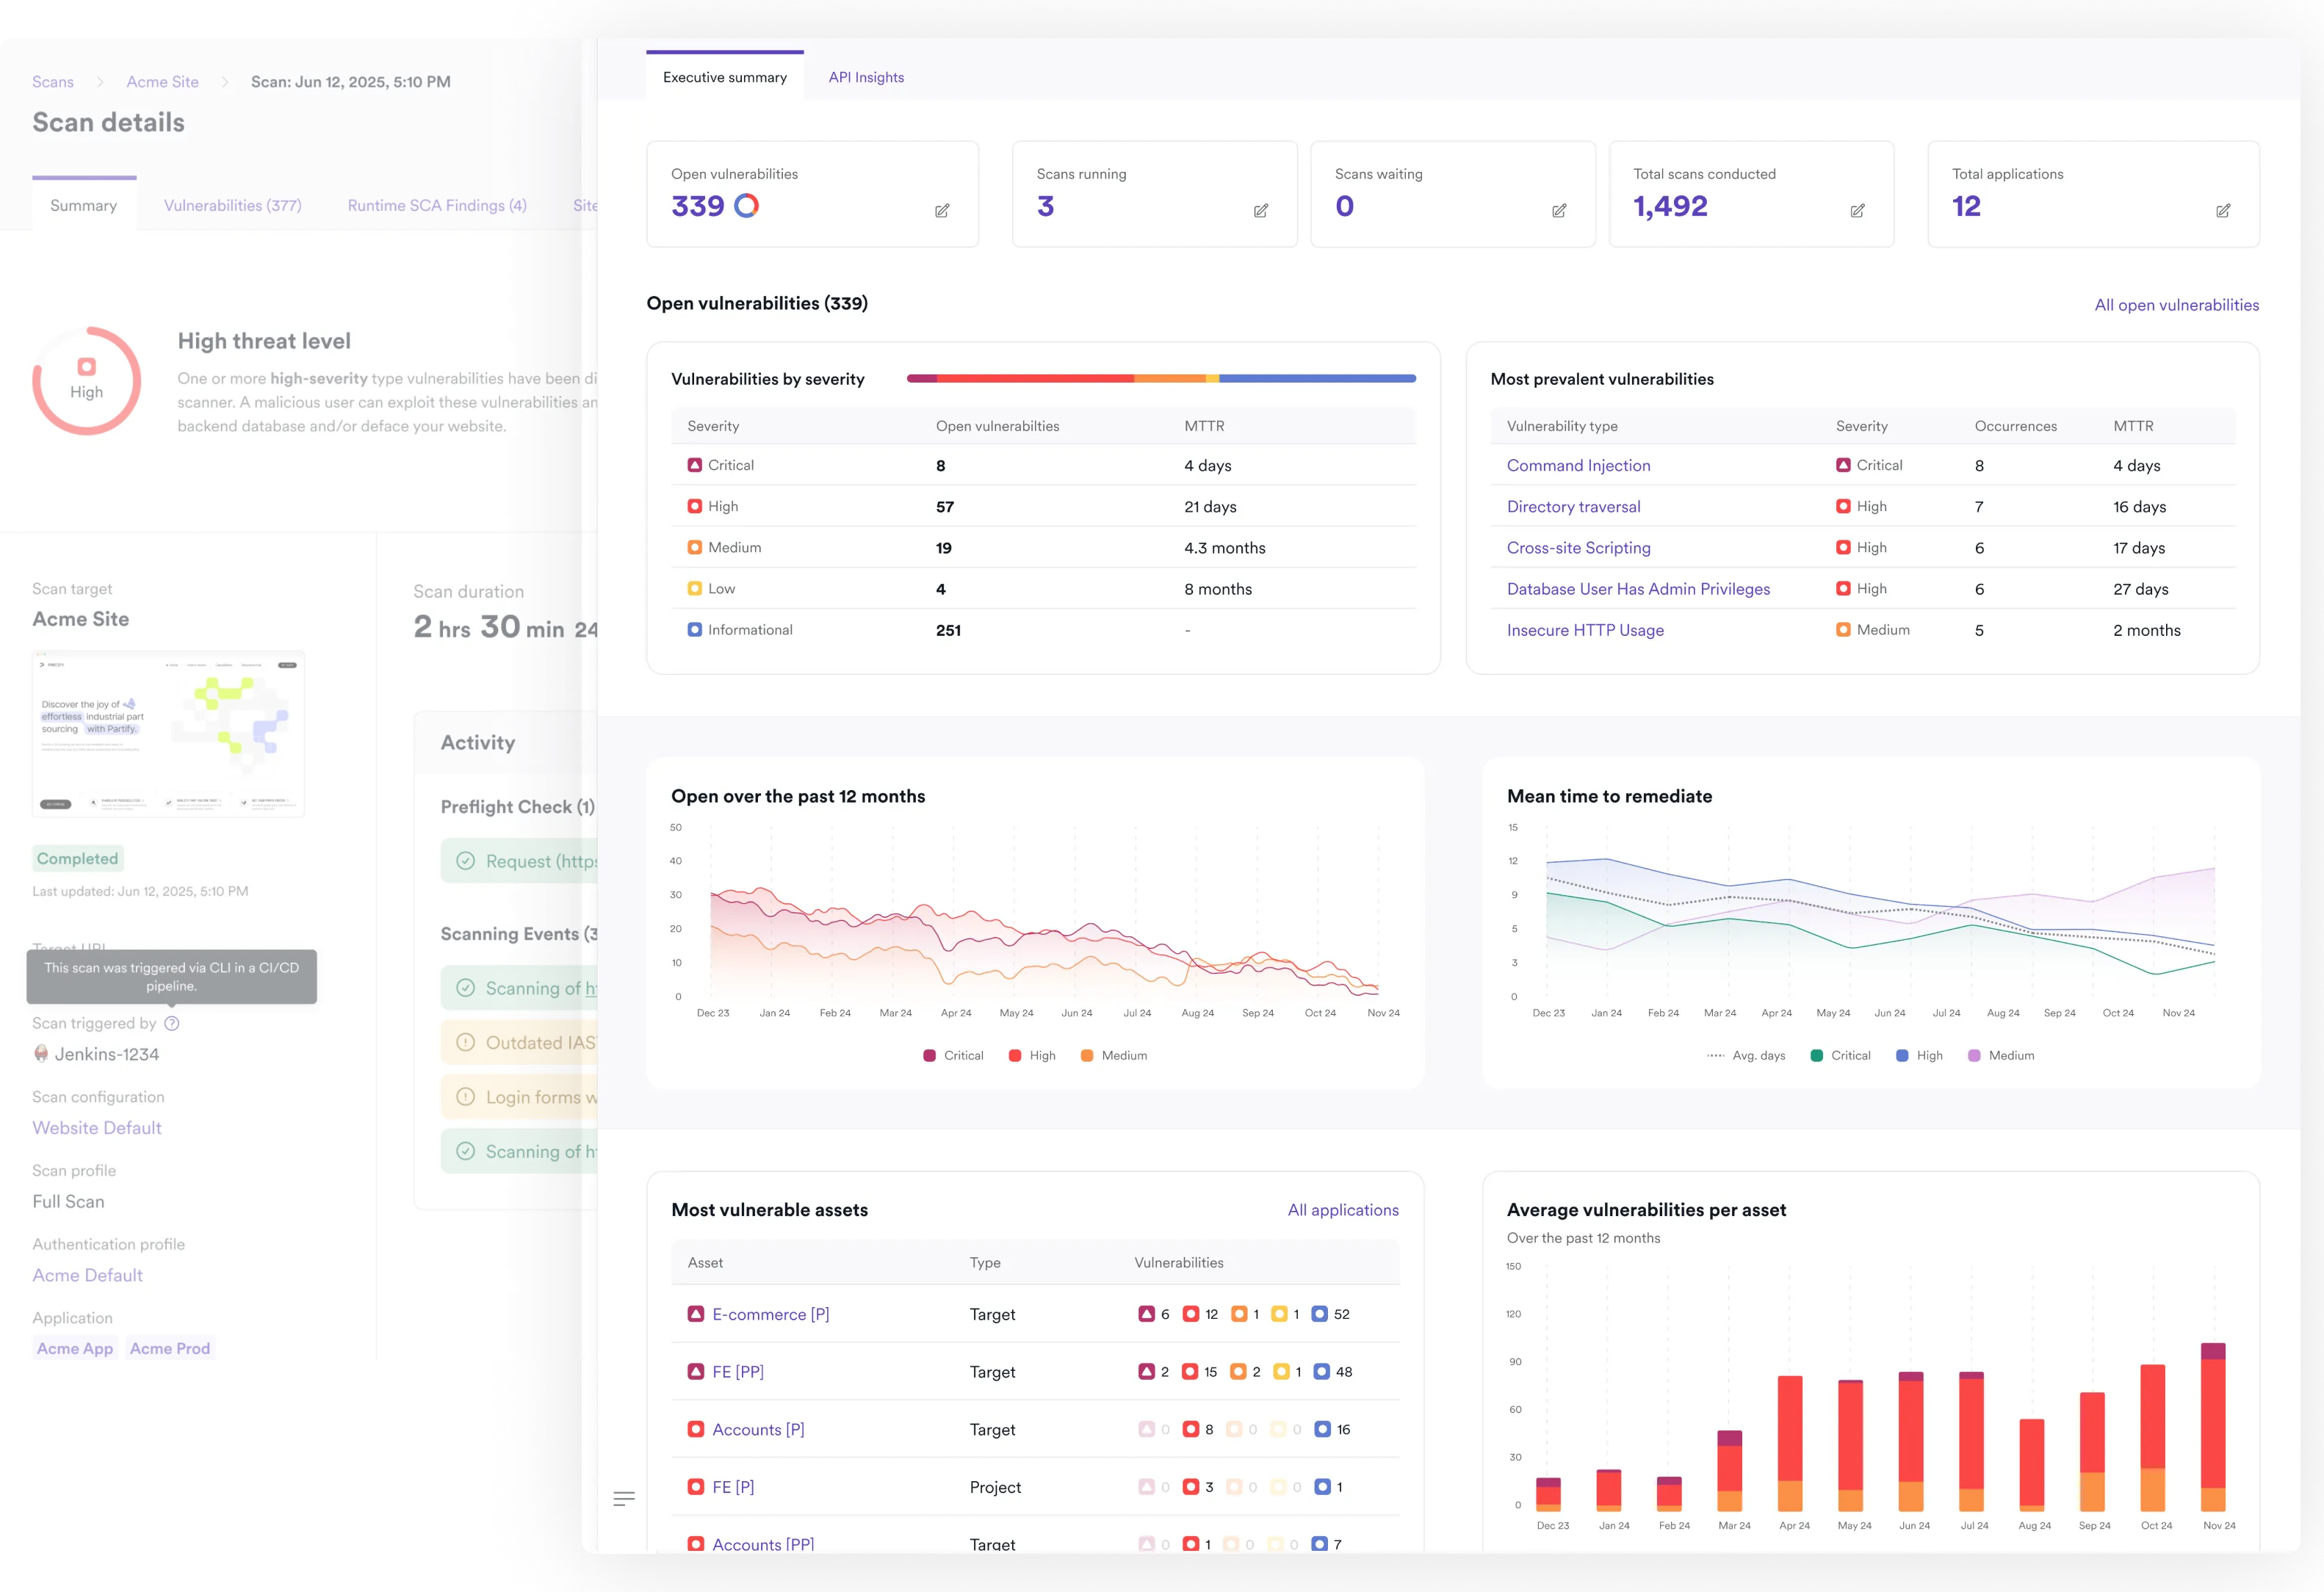
- Confirmed findings: Exploitable issues are verified automatically.
- Clear remediation: Each result links to the affected request and a fix recommendation.
- Less rework: Developers stop closing tickets as false positives.
Speed
Scans that fit your pipeline
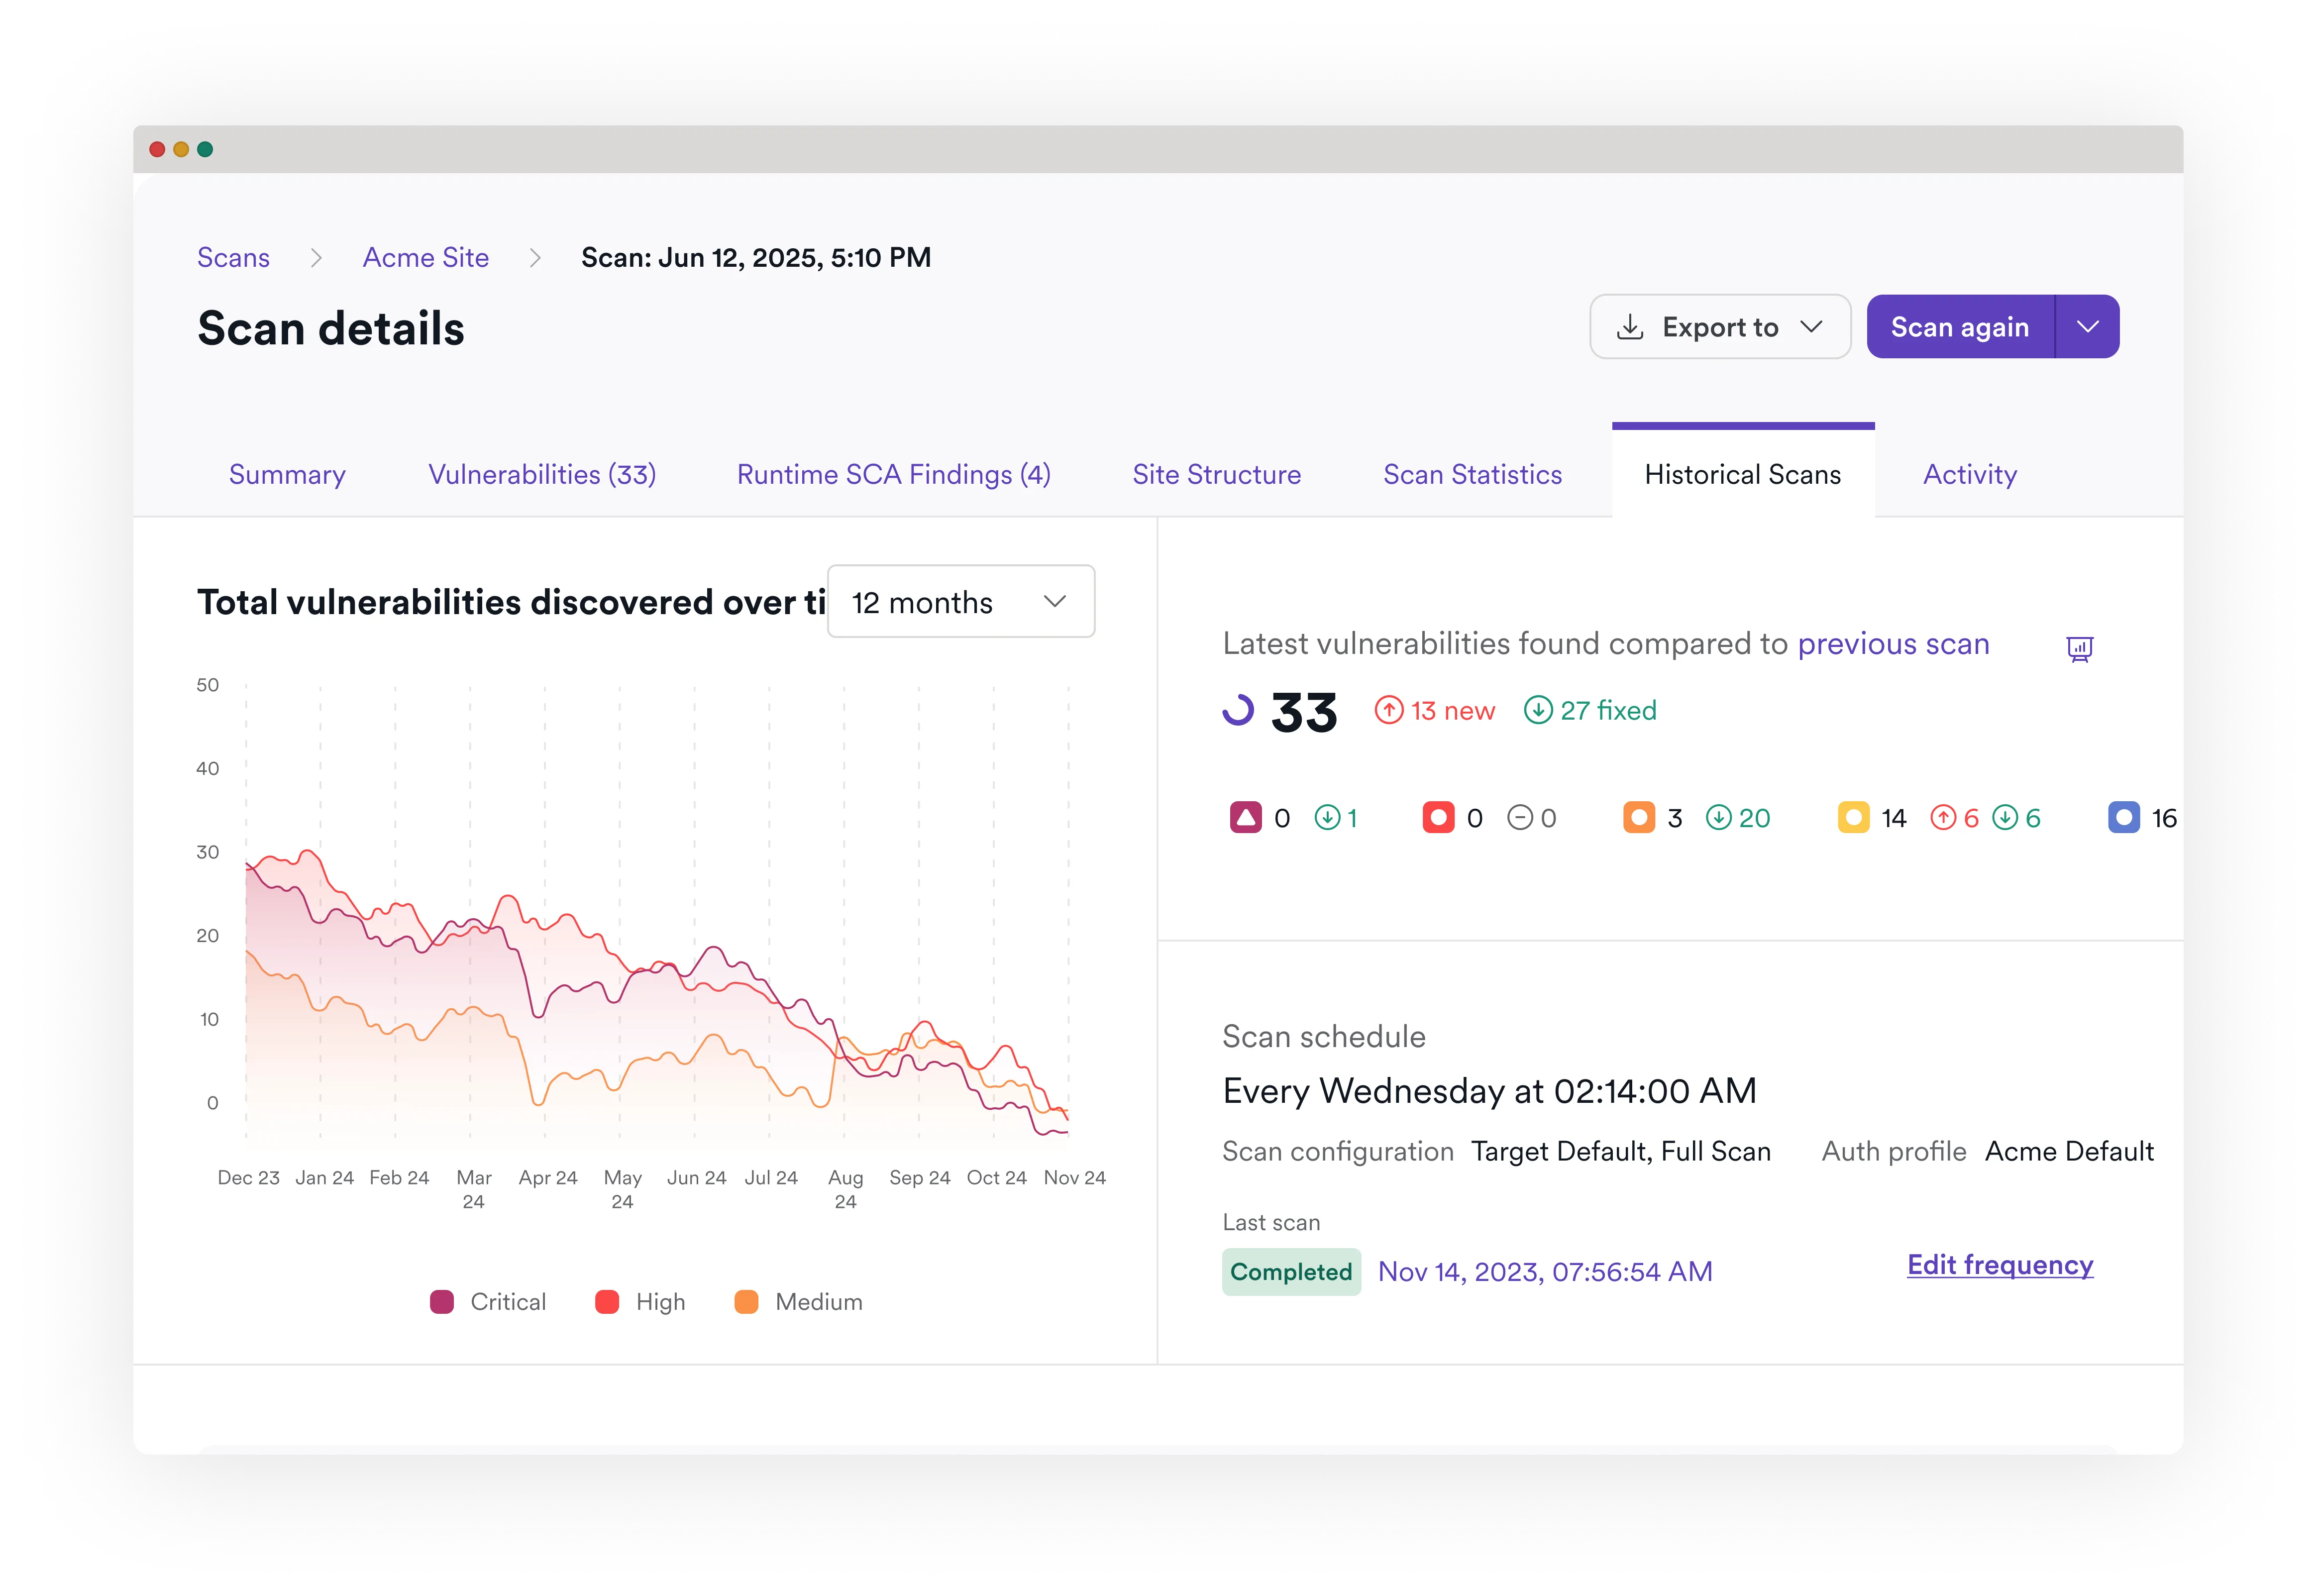
- Incremental scanning: Re-test only what changed.
- Two-way sync: Issues stay current in Jira, GitHub and Azure Boards.
- Policy gates: Fail a build on confirmed critical findings only.
99.98%
Confirmation accuracy for exploitable vulnerabilities
70%
Acceptance rate on AI remediations
40%
More vulnerabilities found compared to leading competitors
Proof-based DAST questions
What is proof-based scanning?
The scanner safely exploits a vulnerability and records the evidence, which confirms the issue is real.
Does it work for APIs?
Yes. REST, SOAP and GraphQL APIs are discovered and tested with the same depth as web applications.
Can it run in CI/CD?
Yes. Scans can be triggered from a pipeline and results synced to your issue tracker.
See it on your own app
Find what is exploitable before attackers do.
Book a DAST demo- Proof of exploit: evidence for every finding
- Fast: results in your pipeline
- Broad: web apps and APIs