Invicti Application Security Platform
All Your Security Signals.
One Platform You Can Trust.
Find every vulnerability, prove what's exploitable, remediate with confidence.
- Industry-leading Web & API DAST: Validate exploitable vulnerabilities with proof-based scanning trusted by thousands of organizations worldwide.
- Runtime-validated prioritization: Correlate DAST, SAST, SCA, IaC, and container security findings to eliminate noise and focus teams on what is actually exploitable.
- Complete application security coverage: Secure web apps, APIs, code, open-source dependencies, infrastructure-as-code, and containers from a single platform.
Get a demo
5000+ Top Organizations Trust Invicti


Most AppSec Platforms Create Noise
Inaccurate, fragmented tools create alert fatigue, slow velocity, and leave teams with no way to measure real progress.

Drowning in alerts
Every scanner floods you with alerts. Without correlation, you waste hours chasing duplicates and false positives.

Always behind dev velocity
With one AppSec engineer for every hundred developers, manual triage and fragmented tools make it impossible to keep up with rapid release cycles.

No remediation metrics
“How long did it take to fix your critical vulnerabilities last quarter?” Most teams can’t answer this simple question, leaving leaders exposed.
Invicti Creates Clarity
Built on the world's most accurate Web & API DAST, Invicti is the only AppSec platform that applies industry-leading runtime intelligence across SAST, SCA, IaC, and container security to shrink your findings backlog down to only the most critical vulnerabilities
Get a demoClarity
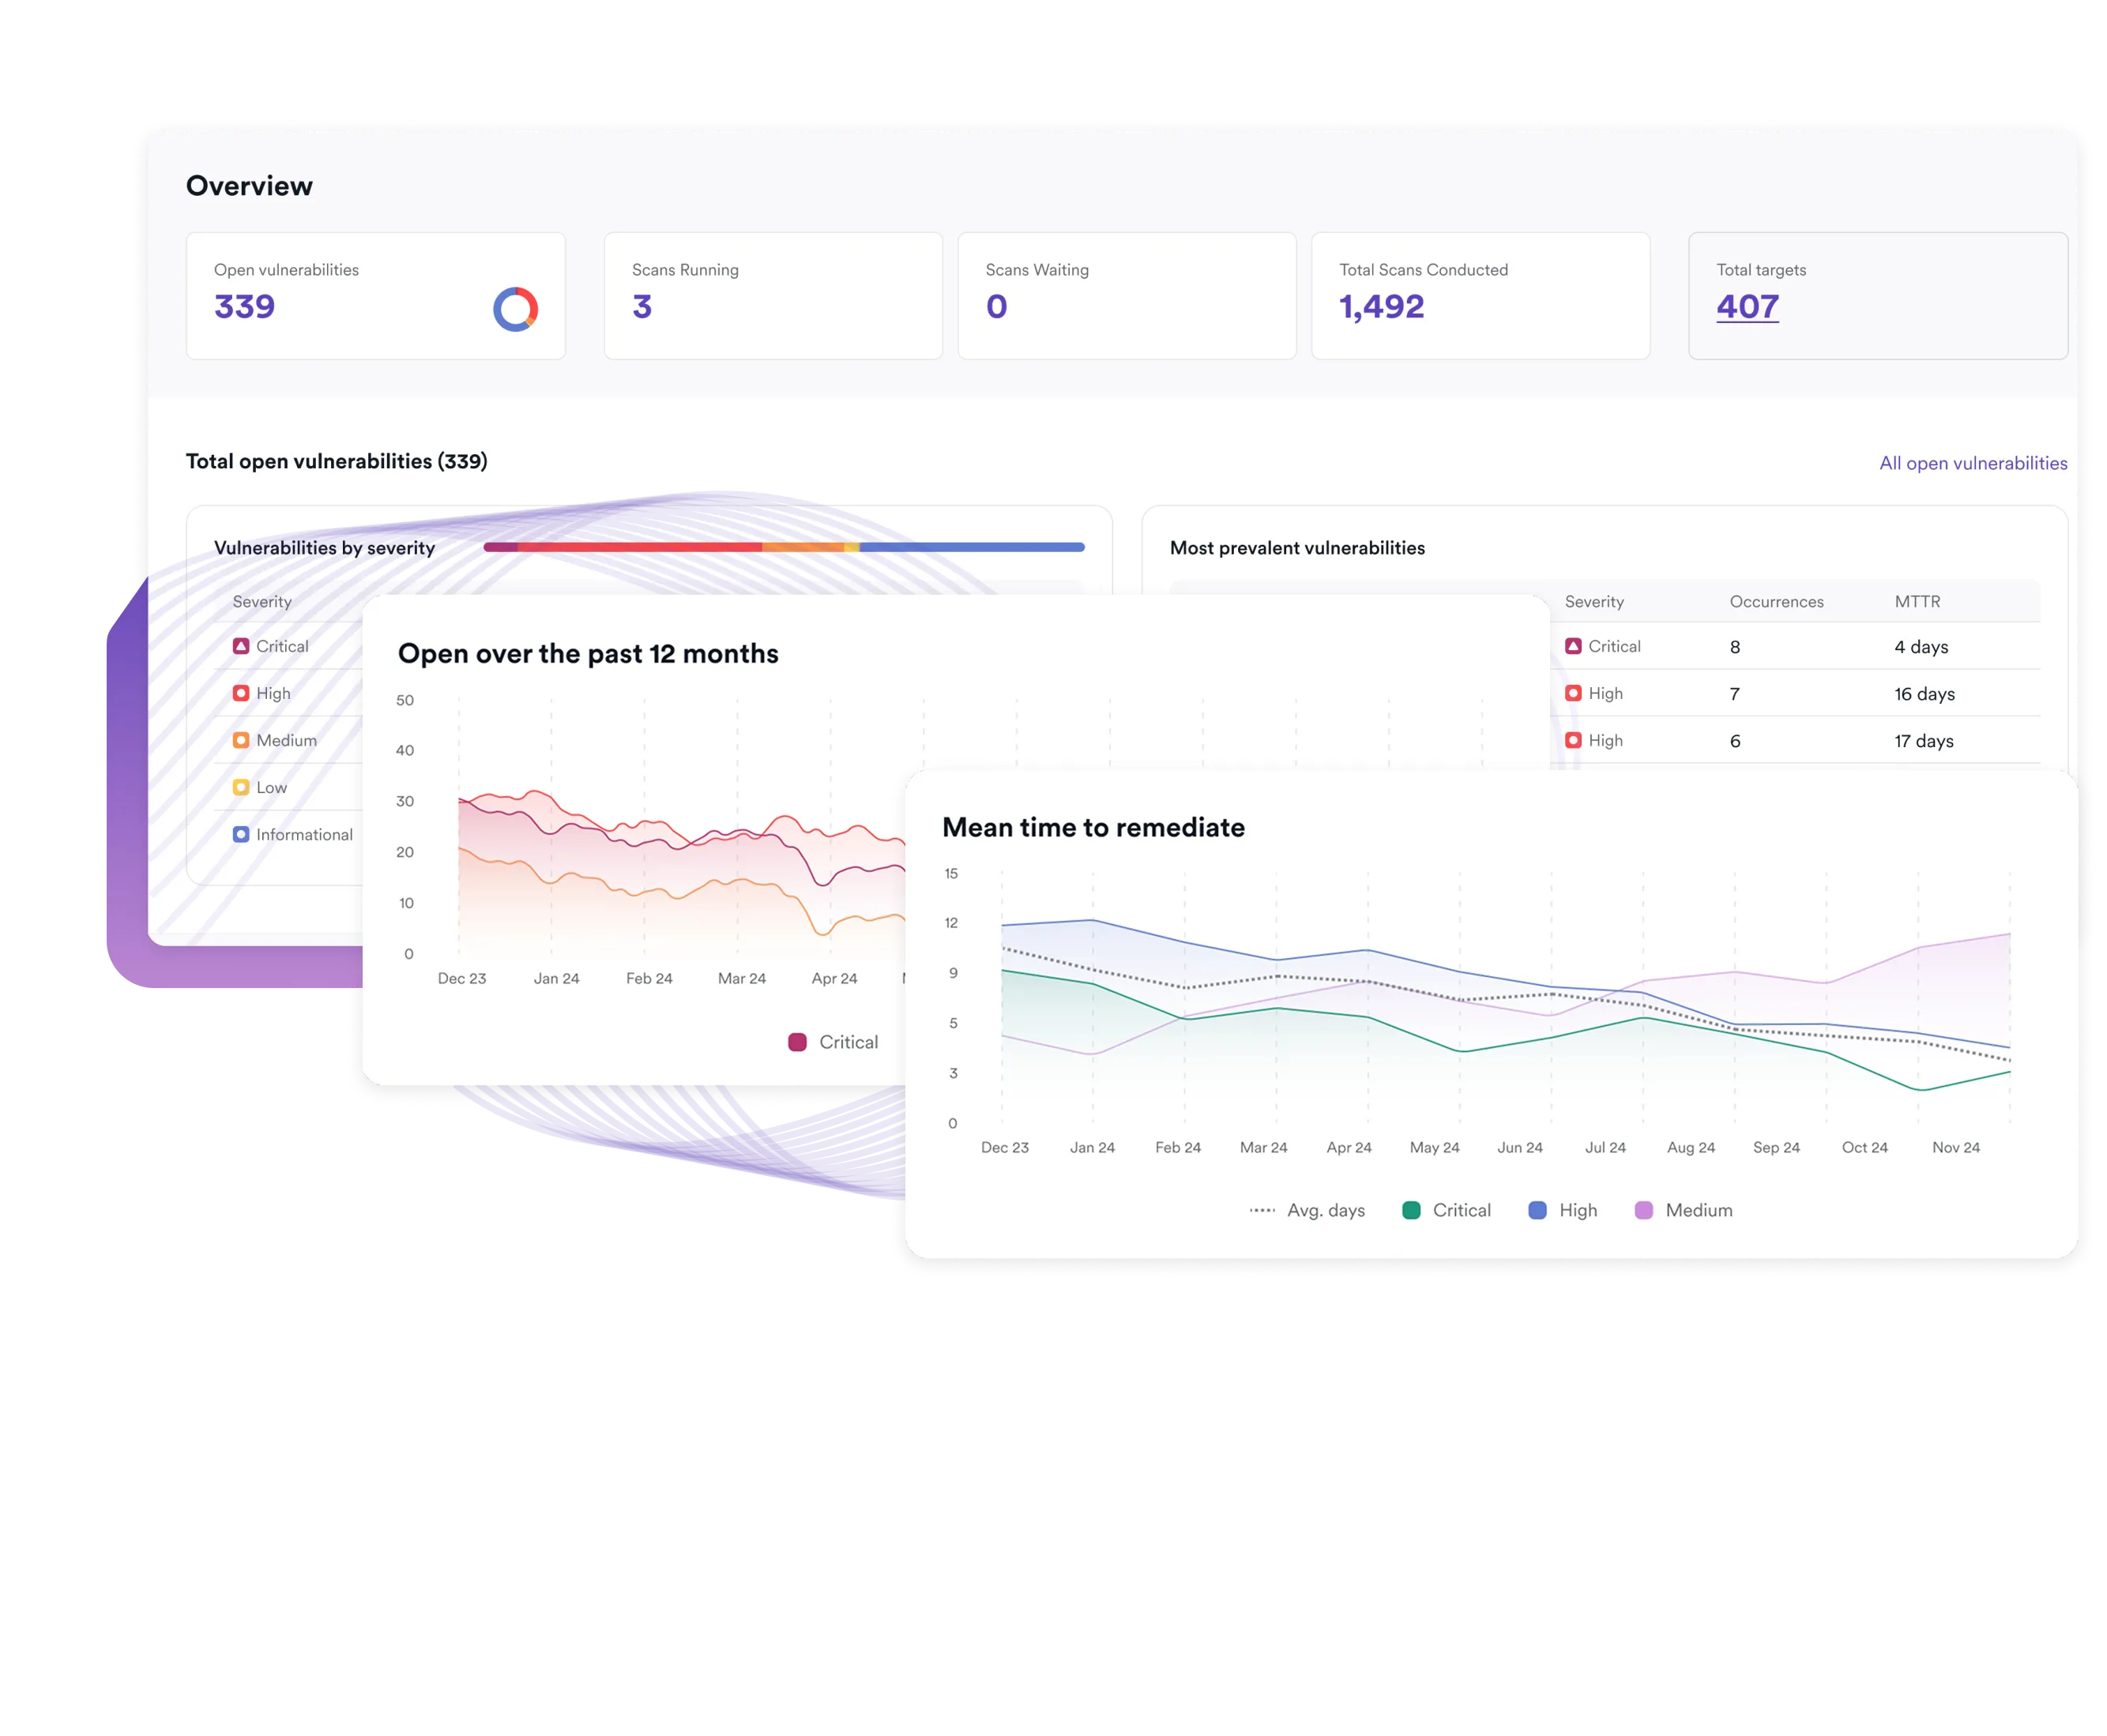
Cut through the noise
- Unified runtime intelligence: A unified AppSec platform where DAST, SAST, SCA, IaC, IAST, and API Security all feed a runtime-validation engine that prioritizes what is actually exploitable.
- Web & API DAST leader: Find and test every web app and API with multi-layer discovery and proof-based scanning.
- Correlate across scanners: Invicti ASPM correlates issues across tools into a single, prioritized risk view.
- Suppress noise: Deduplicate alerts, create custom suppression rules, and escalate only real runtime-verified findings.
- Threat intelligence: Automatically adjust the risk scores of vulnerabilities based on your threat Intelligence data.
Speed
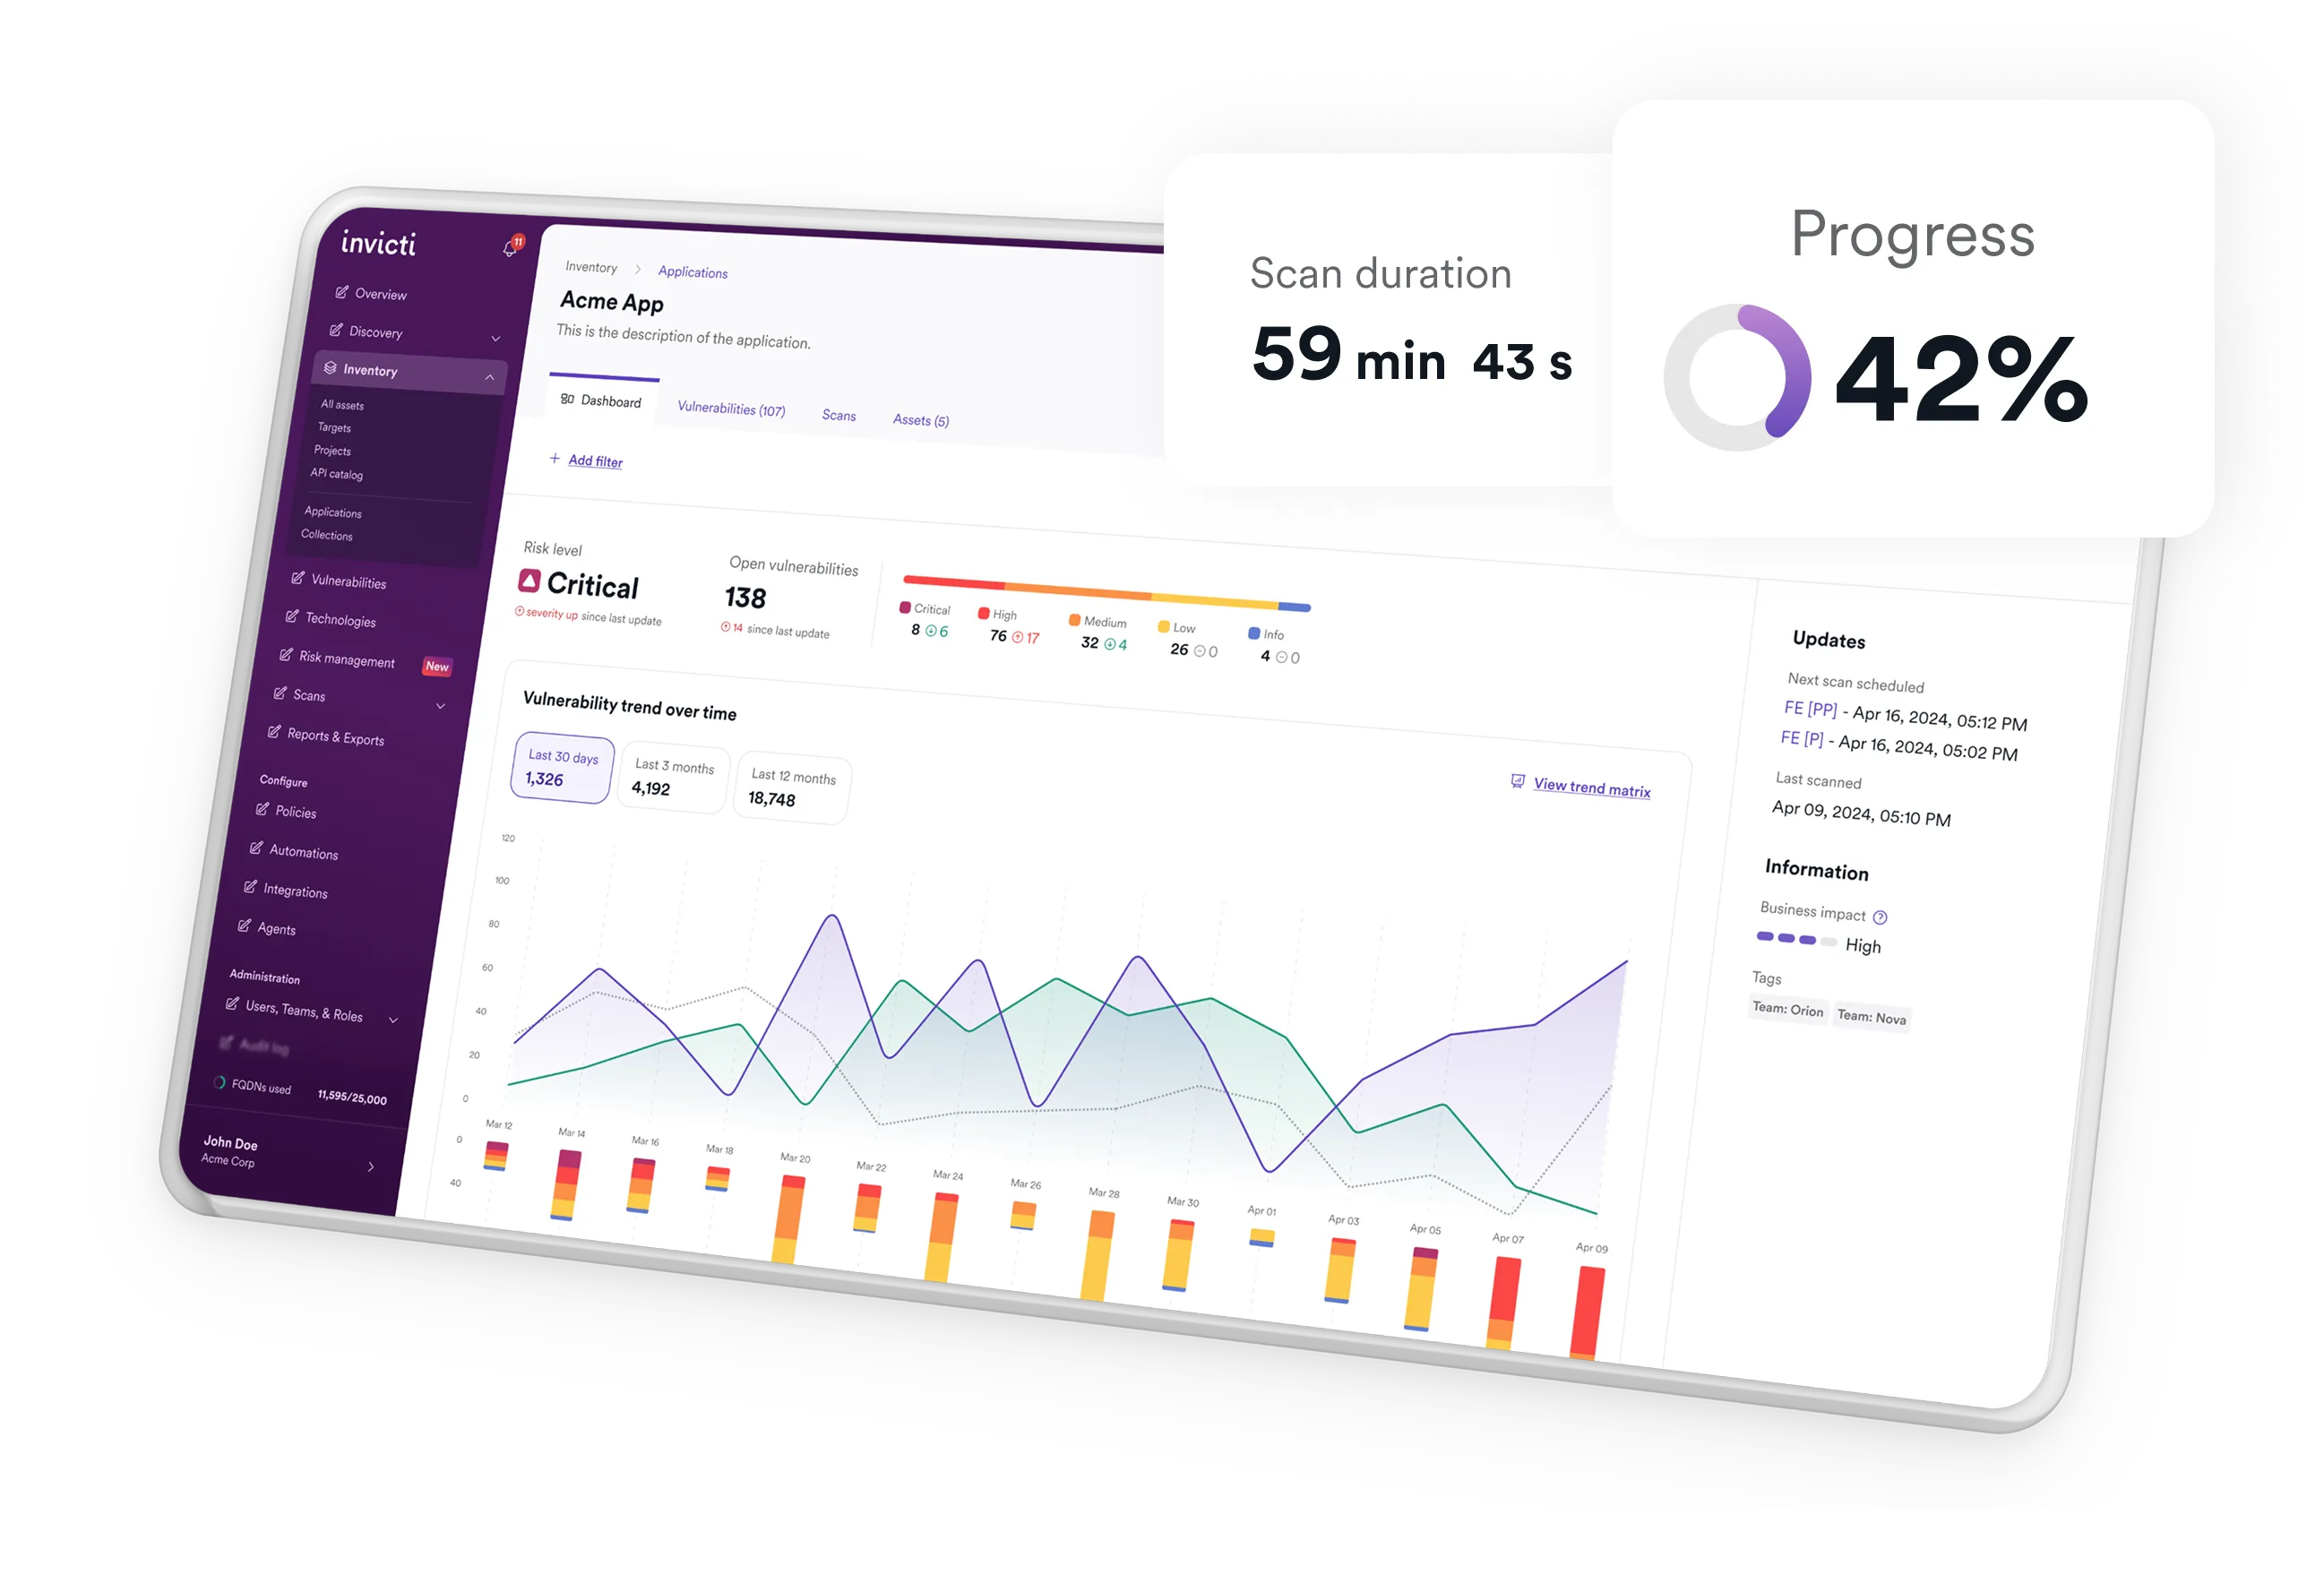
Keep up with development
- Auto-correlate DAST and SAST findings: Map verified runtime vulnerabilities directly to the source code, developers, and remediation steps needed to fix them.
- Trigger workflows automatically: Run scans, imports, and escalations without manual overhead.
- Remediate with AI guidance: Provide developers with step-by-step fixes, reducing back-and-forth.
- Integrate directly with dev tools: Two-way sync with Jira, GitHub, and Azure Boards keeps issues current until resolved.
confidence
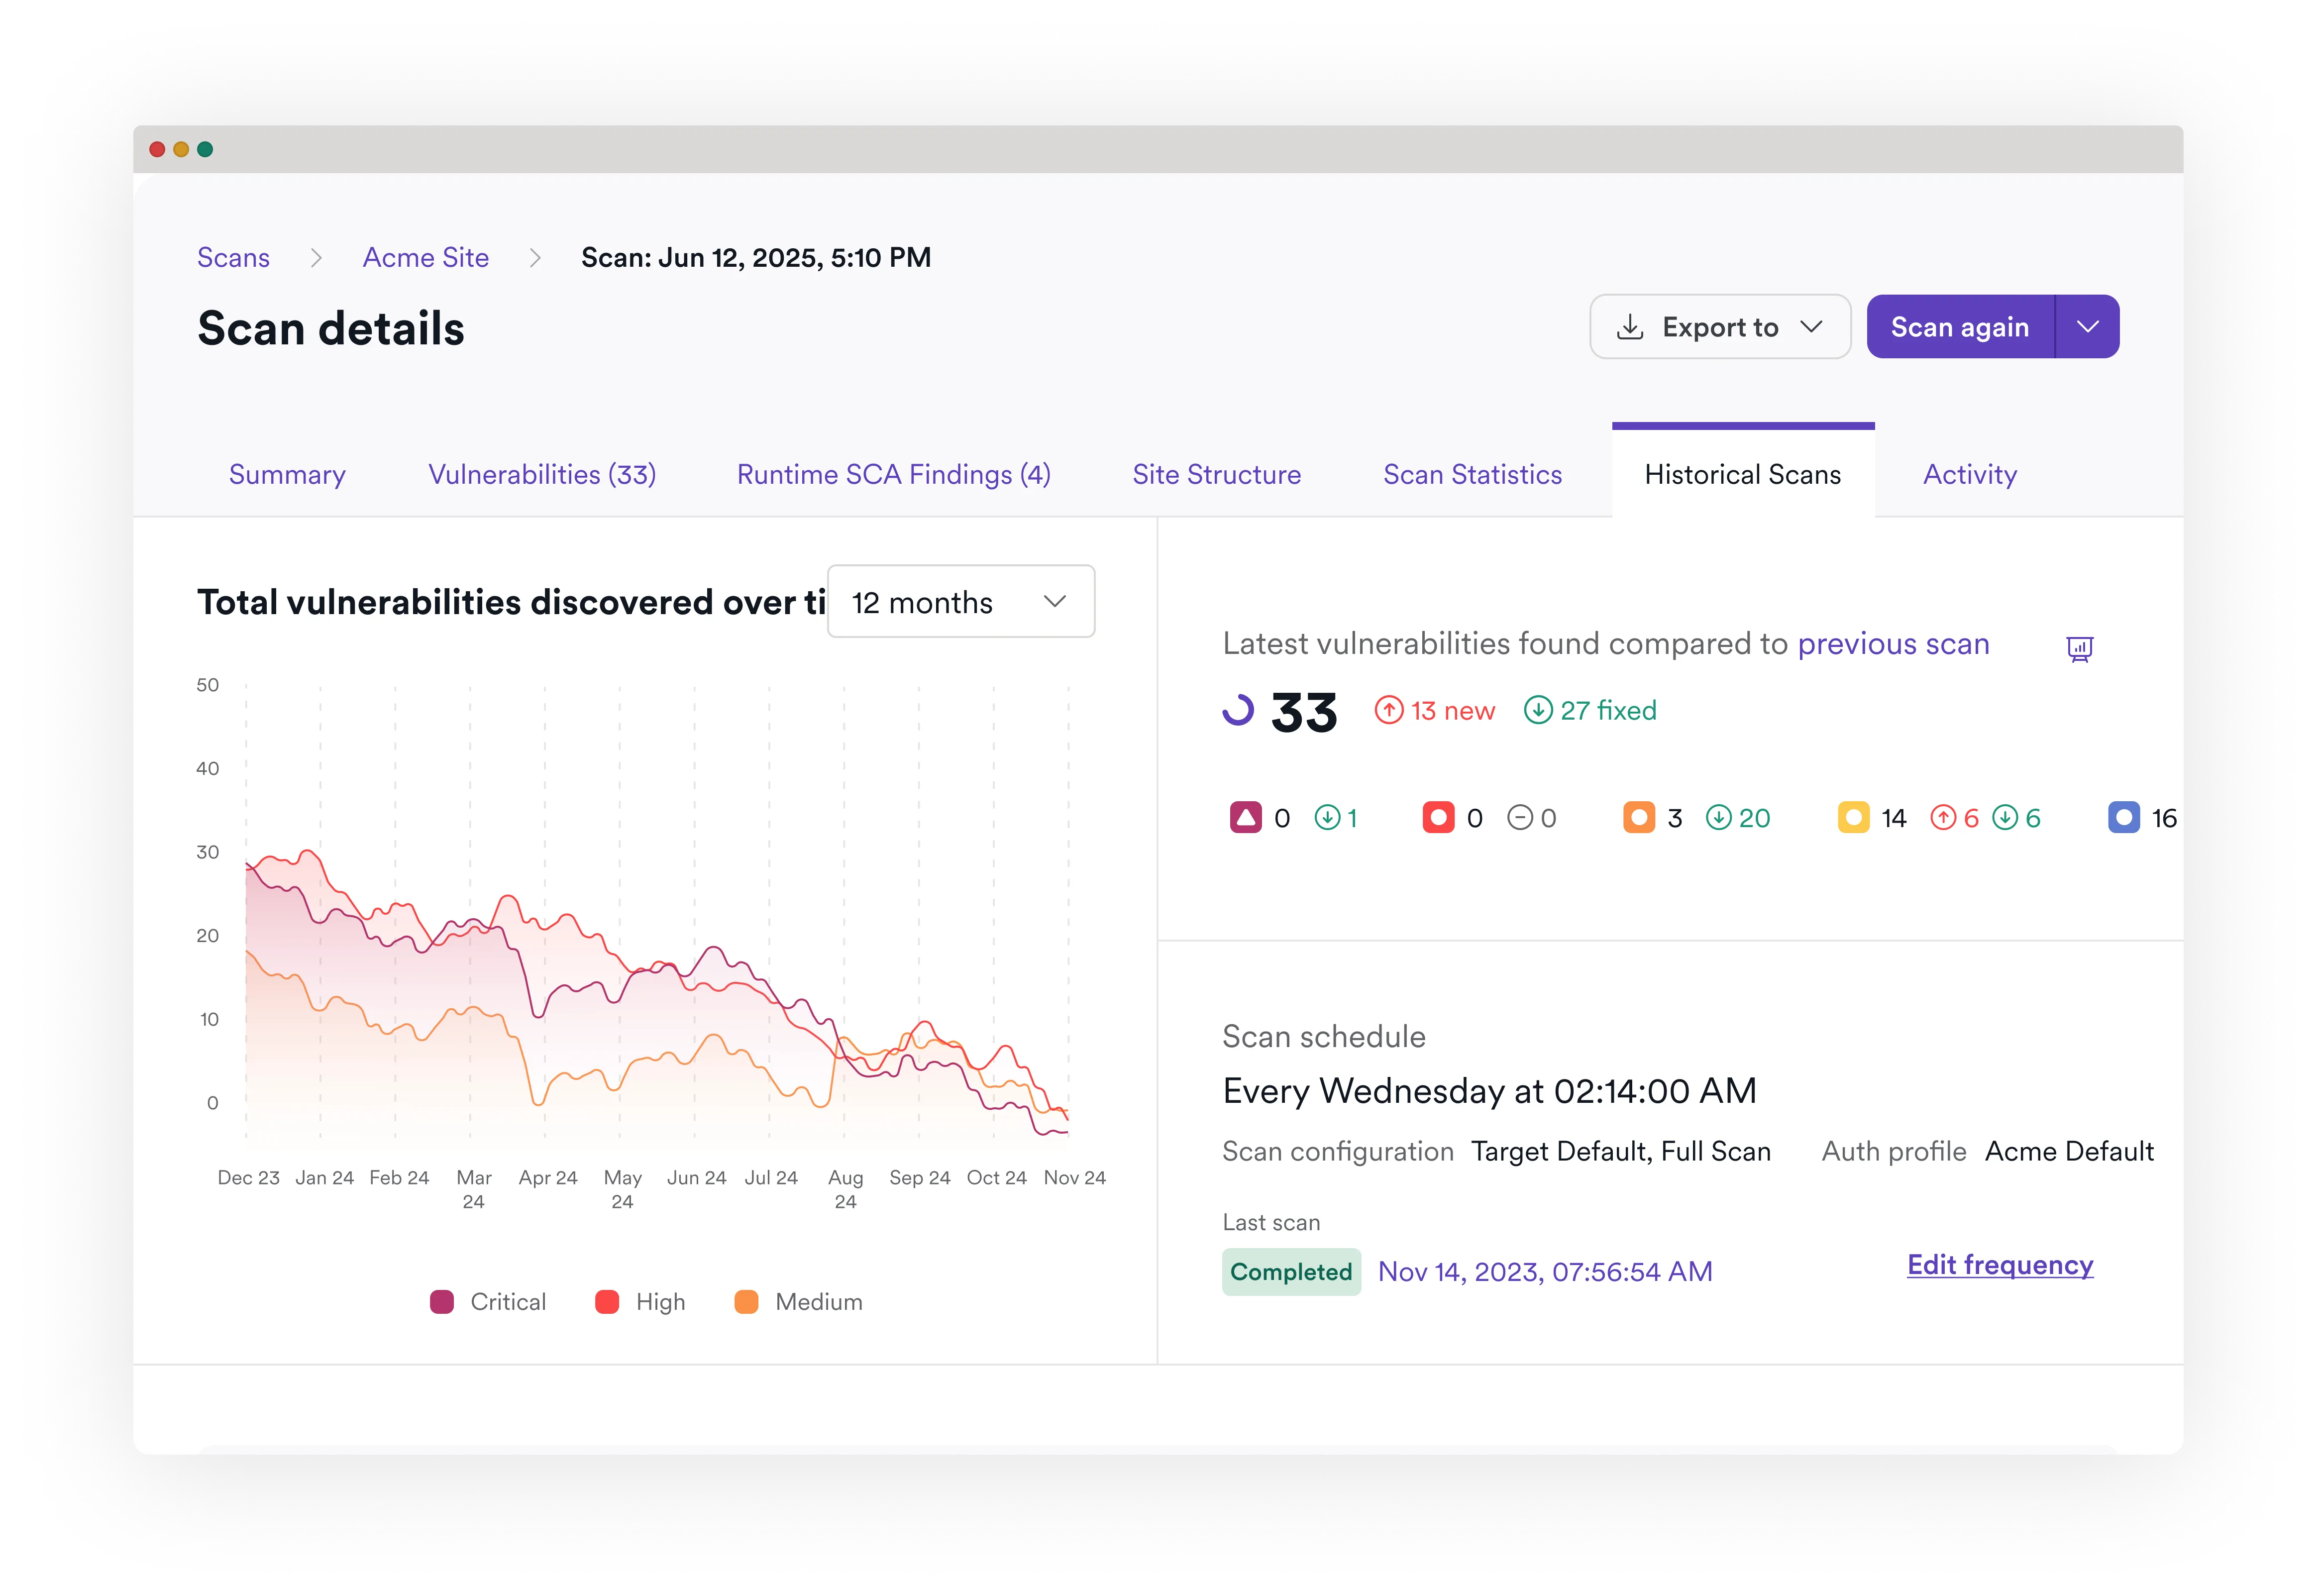
Know where you stand
- Track remediation metrics: Measure time-to-triage and time-to-fix across projects and teams.
- Maintain corporate memory: Preserve historical vulnerability data even when you change tools.
- Assign the right access: Role-based permissions ensure every stakeholder sees only the data that matters to them.
- Report with confidence: Generate dashboards and compliance reports for executives, auditors, and developers.
- Prove progress over time: Monitor posture trends to replace guesswork with measurable improvement.
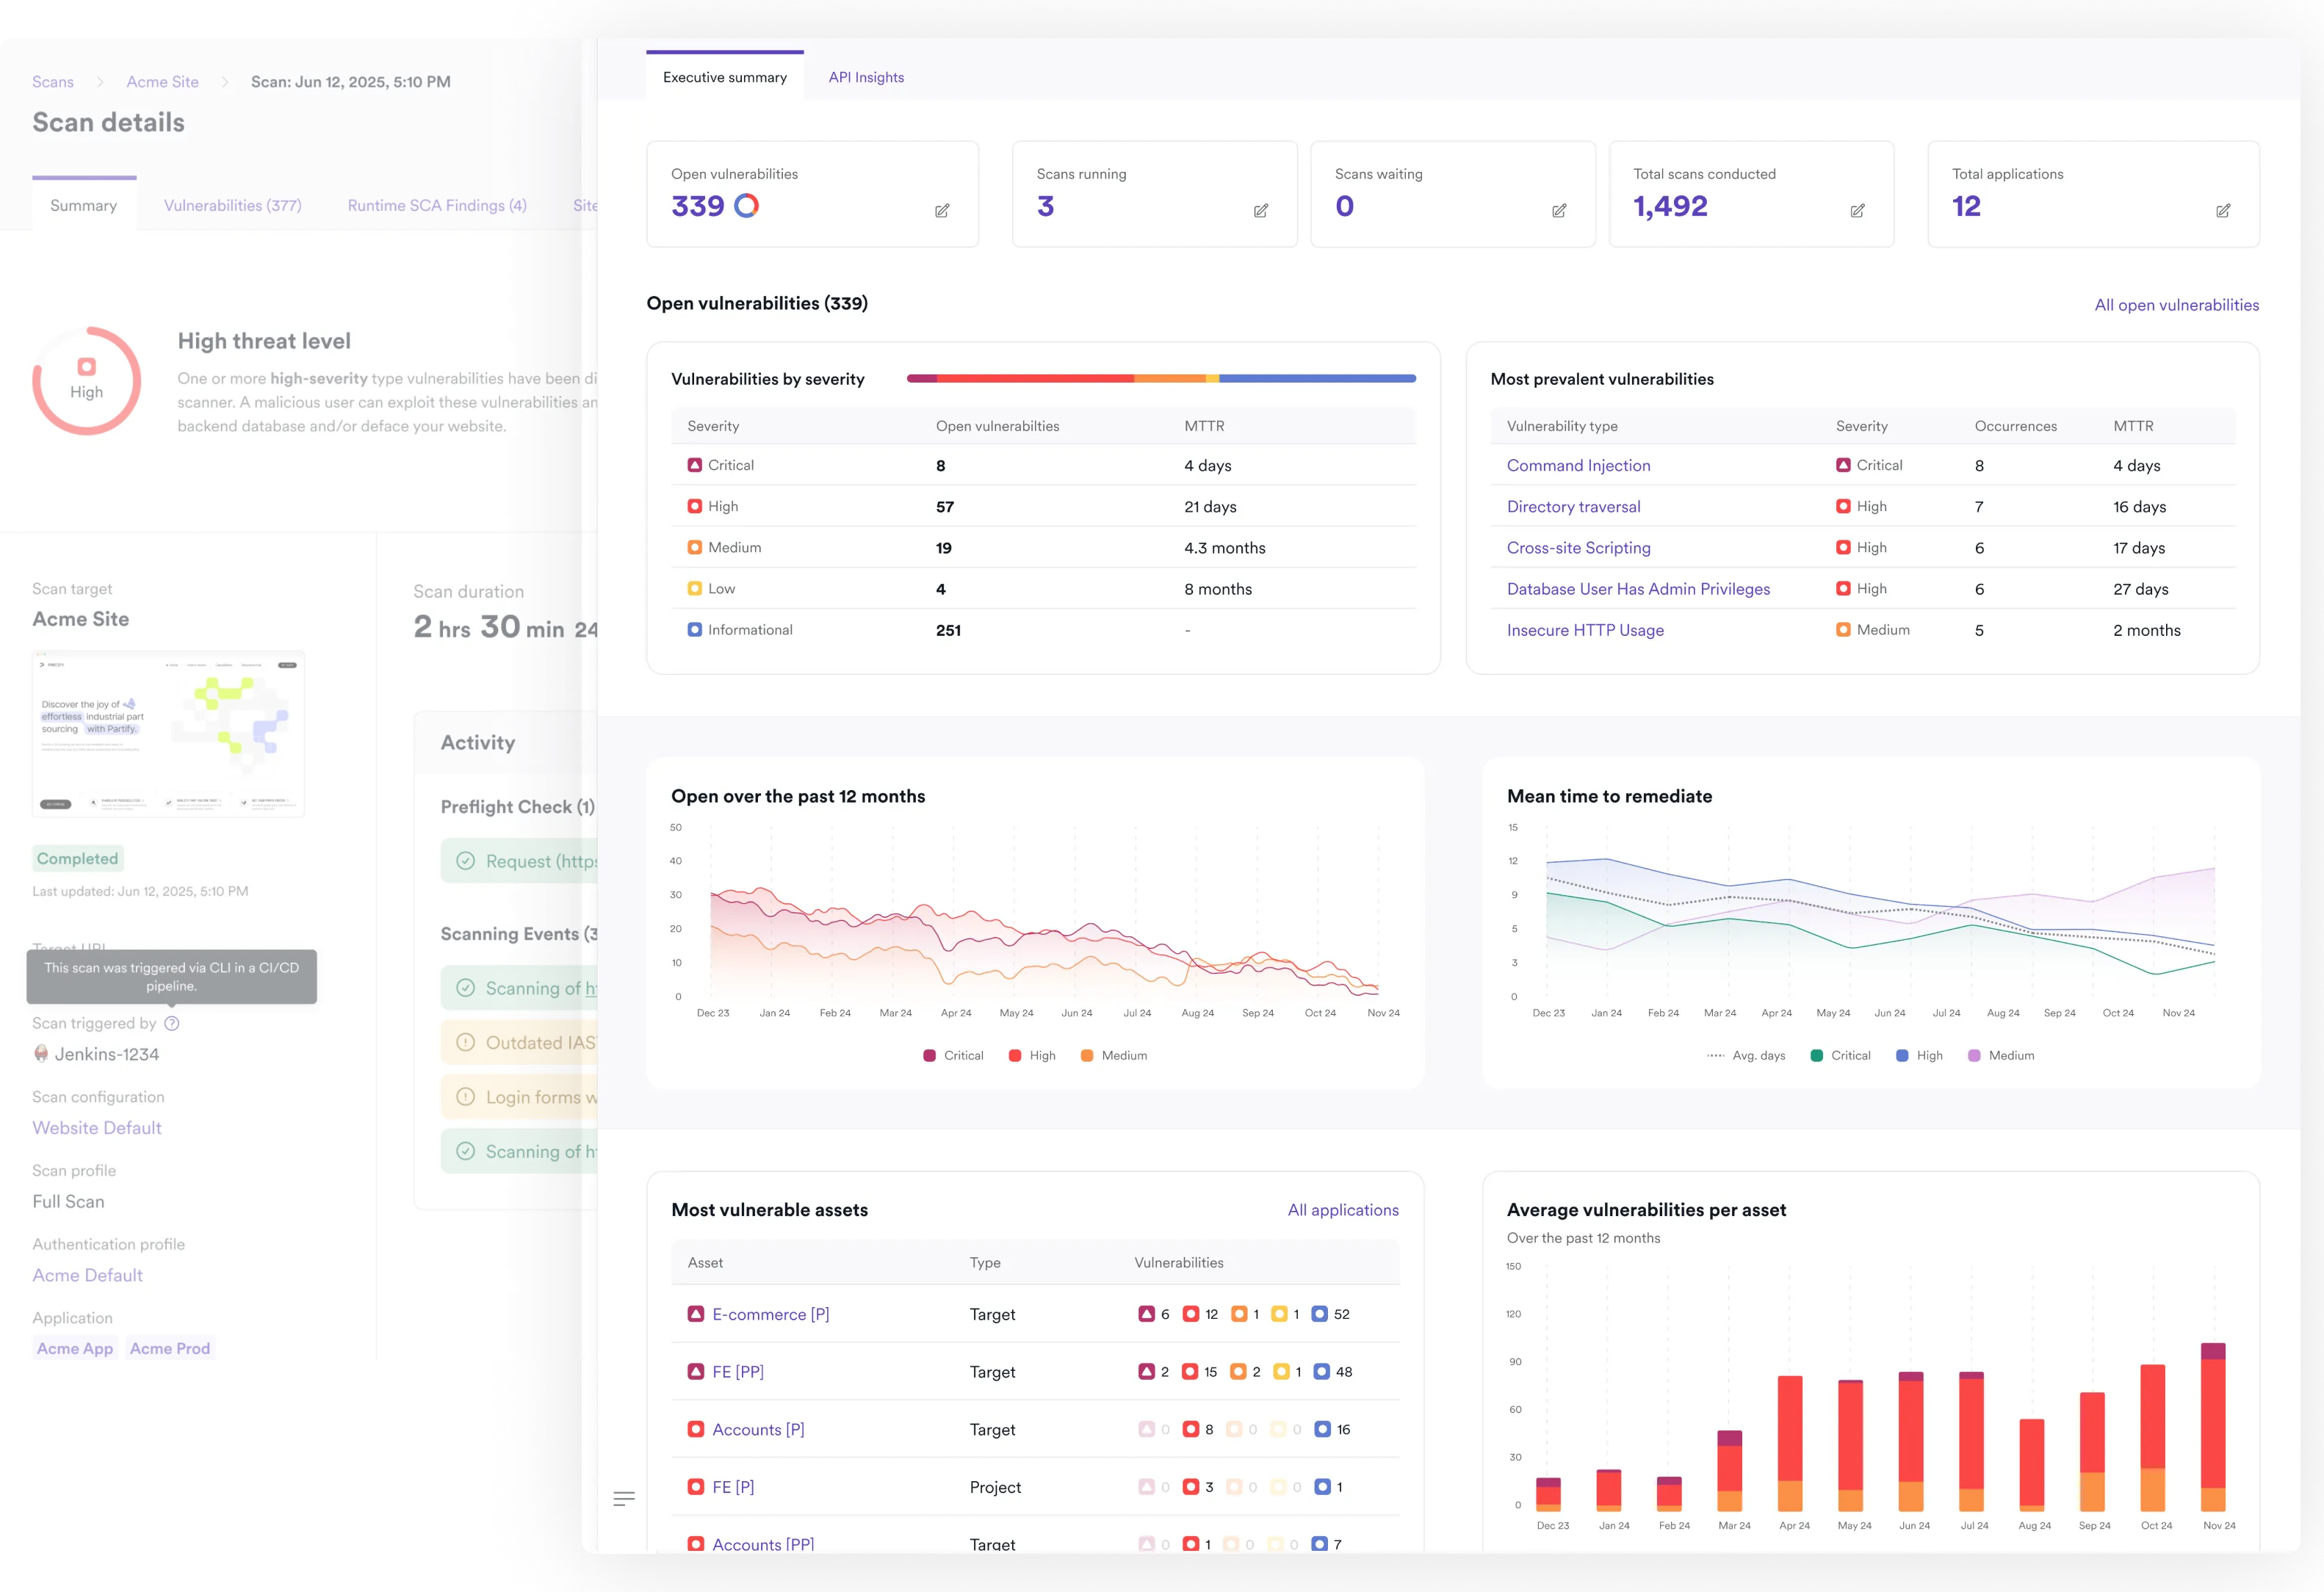
All Scan Types, Verified in a Single View
Invicti delivers industry-best AST, leading ASPM functionality, and complete integration with all the tools you already use.
Get a demoSAST
Find, validate, and fix code vulnerabilities
Invicti SAST moves beyond theoretical findings by connecting static analysis to verified runtime vulnerabilities, code ownership, and remediation guidance.
Get a demo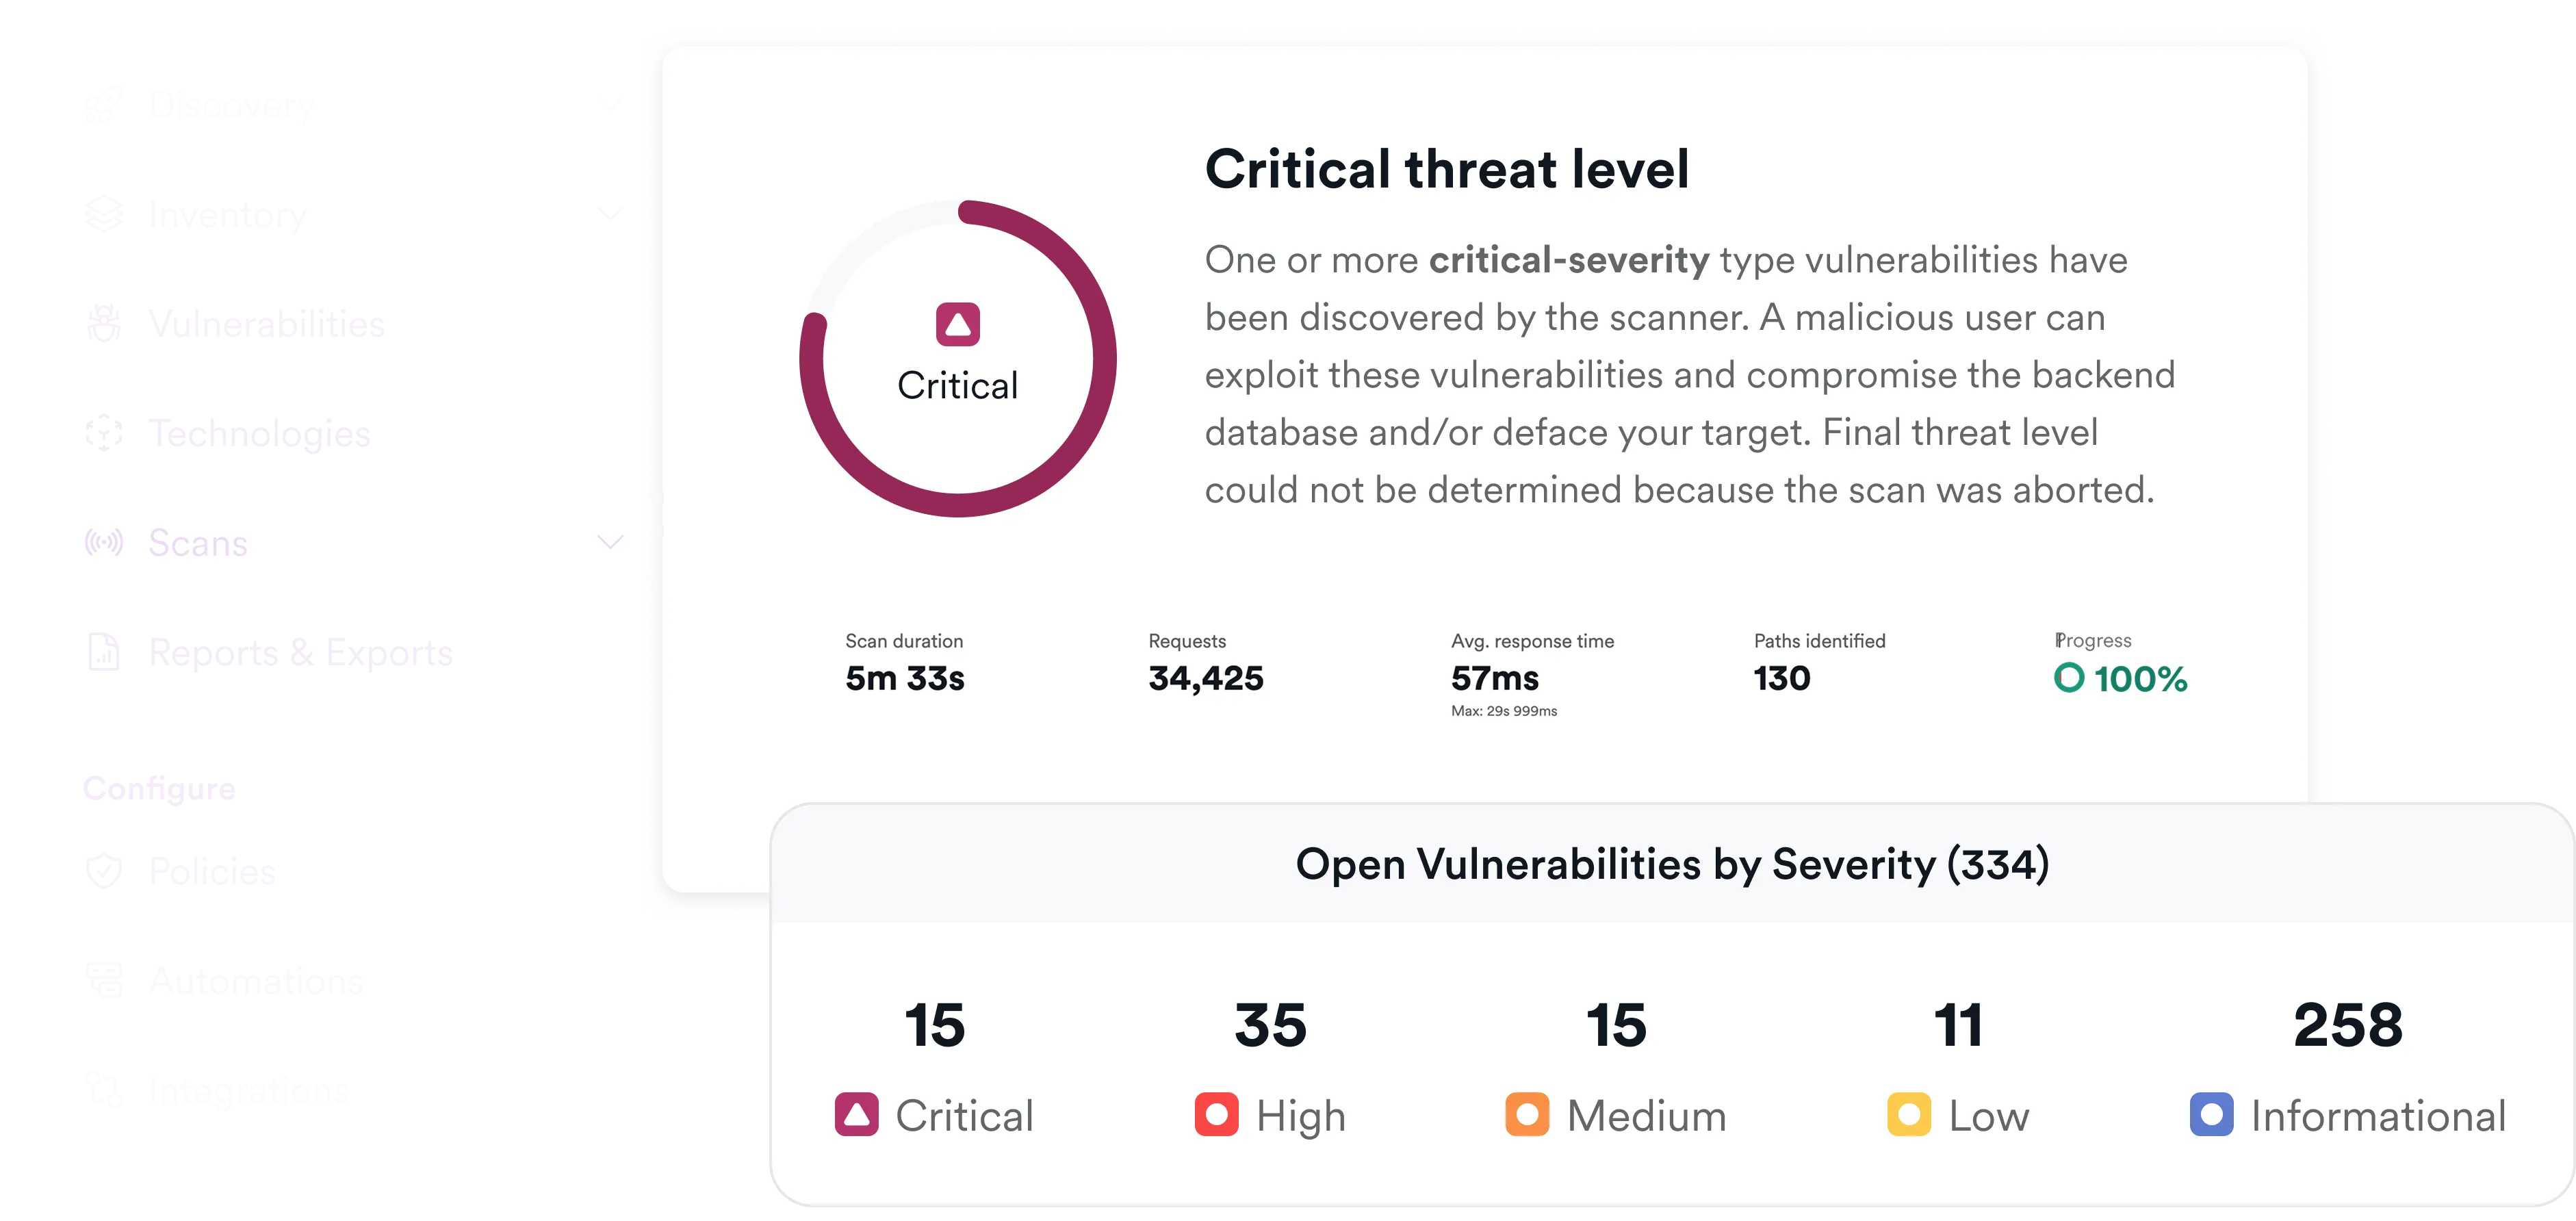
SCA
Take control of open-source risk
Discover vulnerable dependencies, generate SBOMs, identify container risks, and prioritize remediation with runtime intelligence.
Get a demo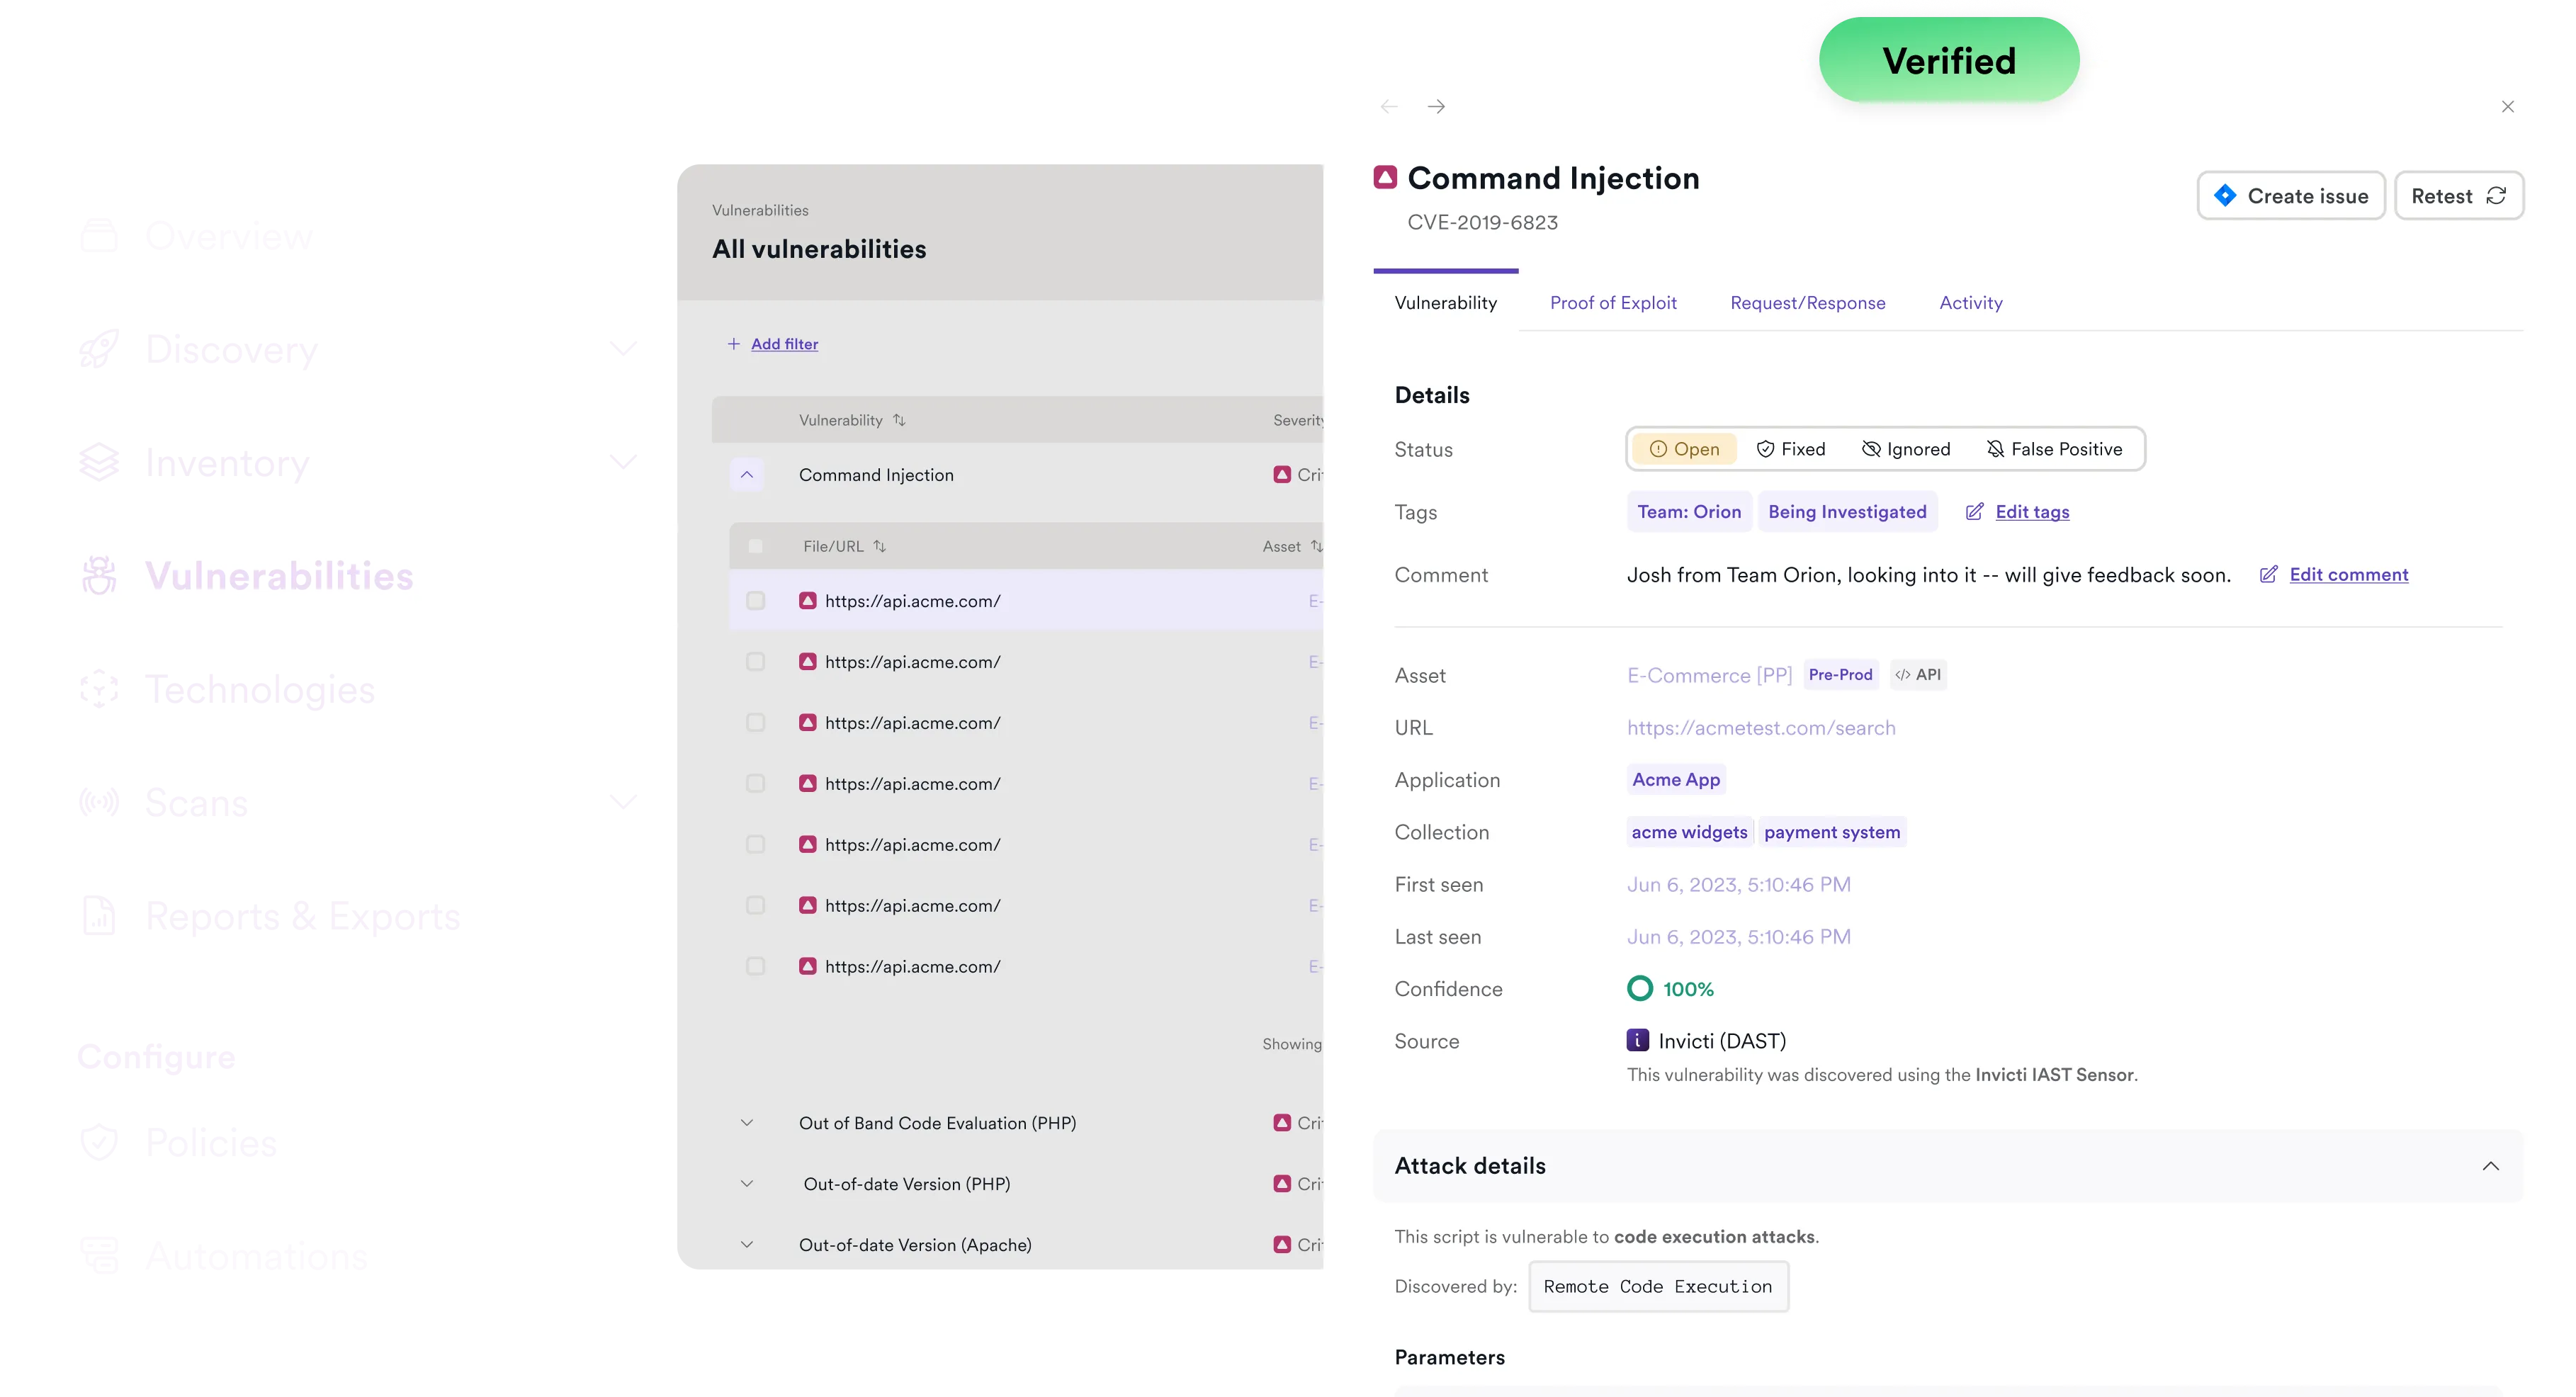
Container Security
Full visibility, smarter workflows, stronger container security
Secure containerized applications with image scanning, software supply chain analysis, and runtime-informed prioritization that cuts through vulnerability noise.
Get a demo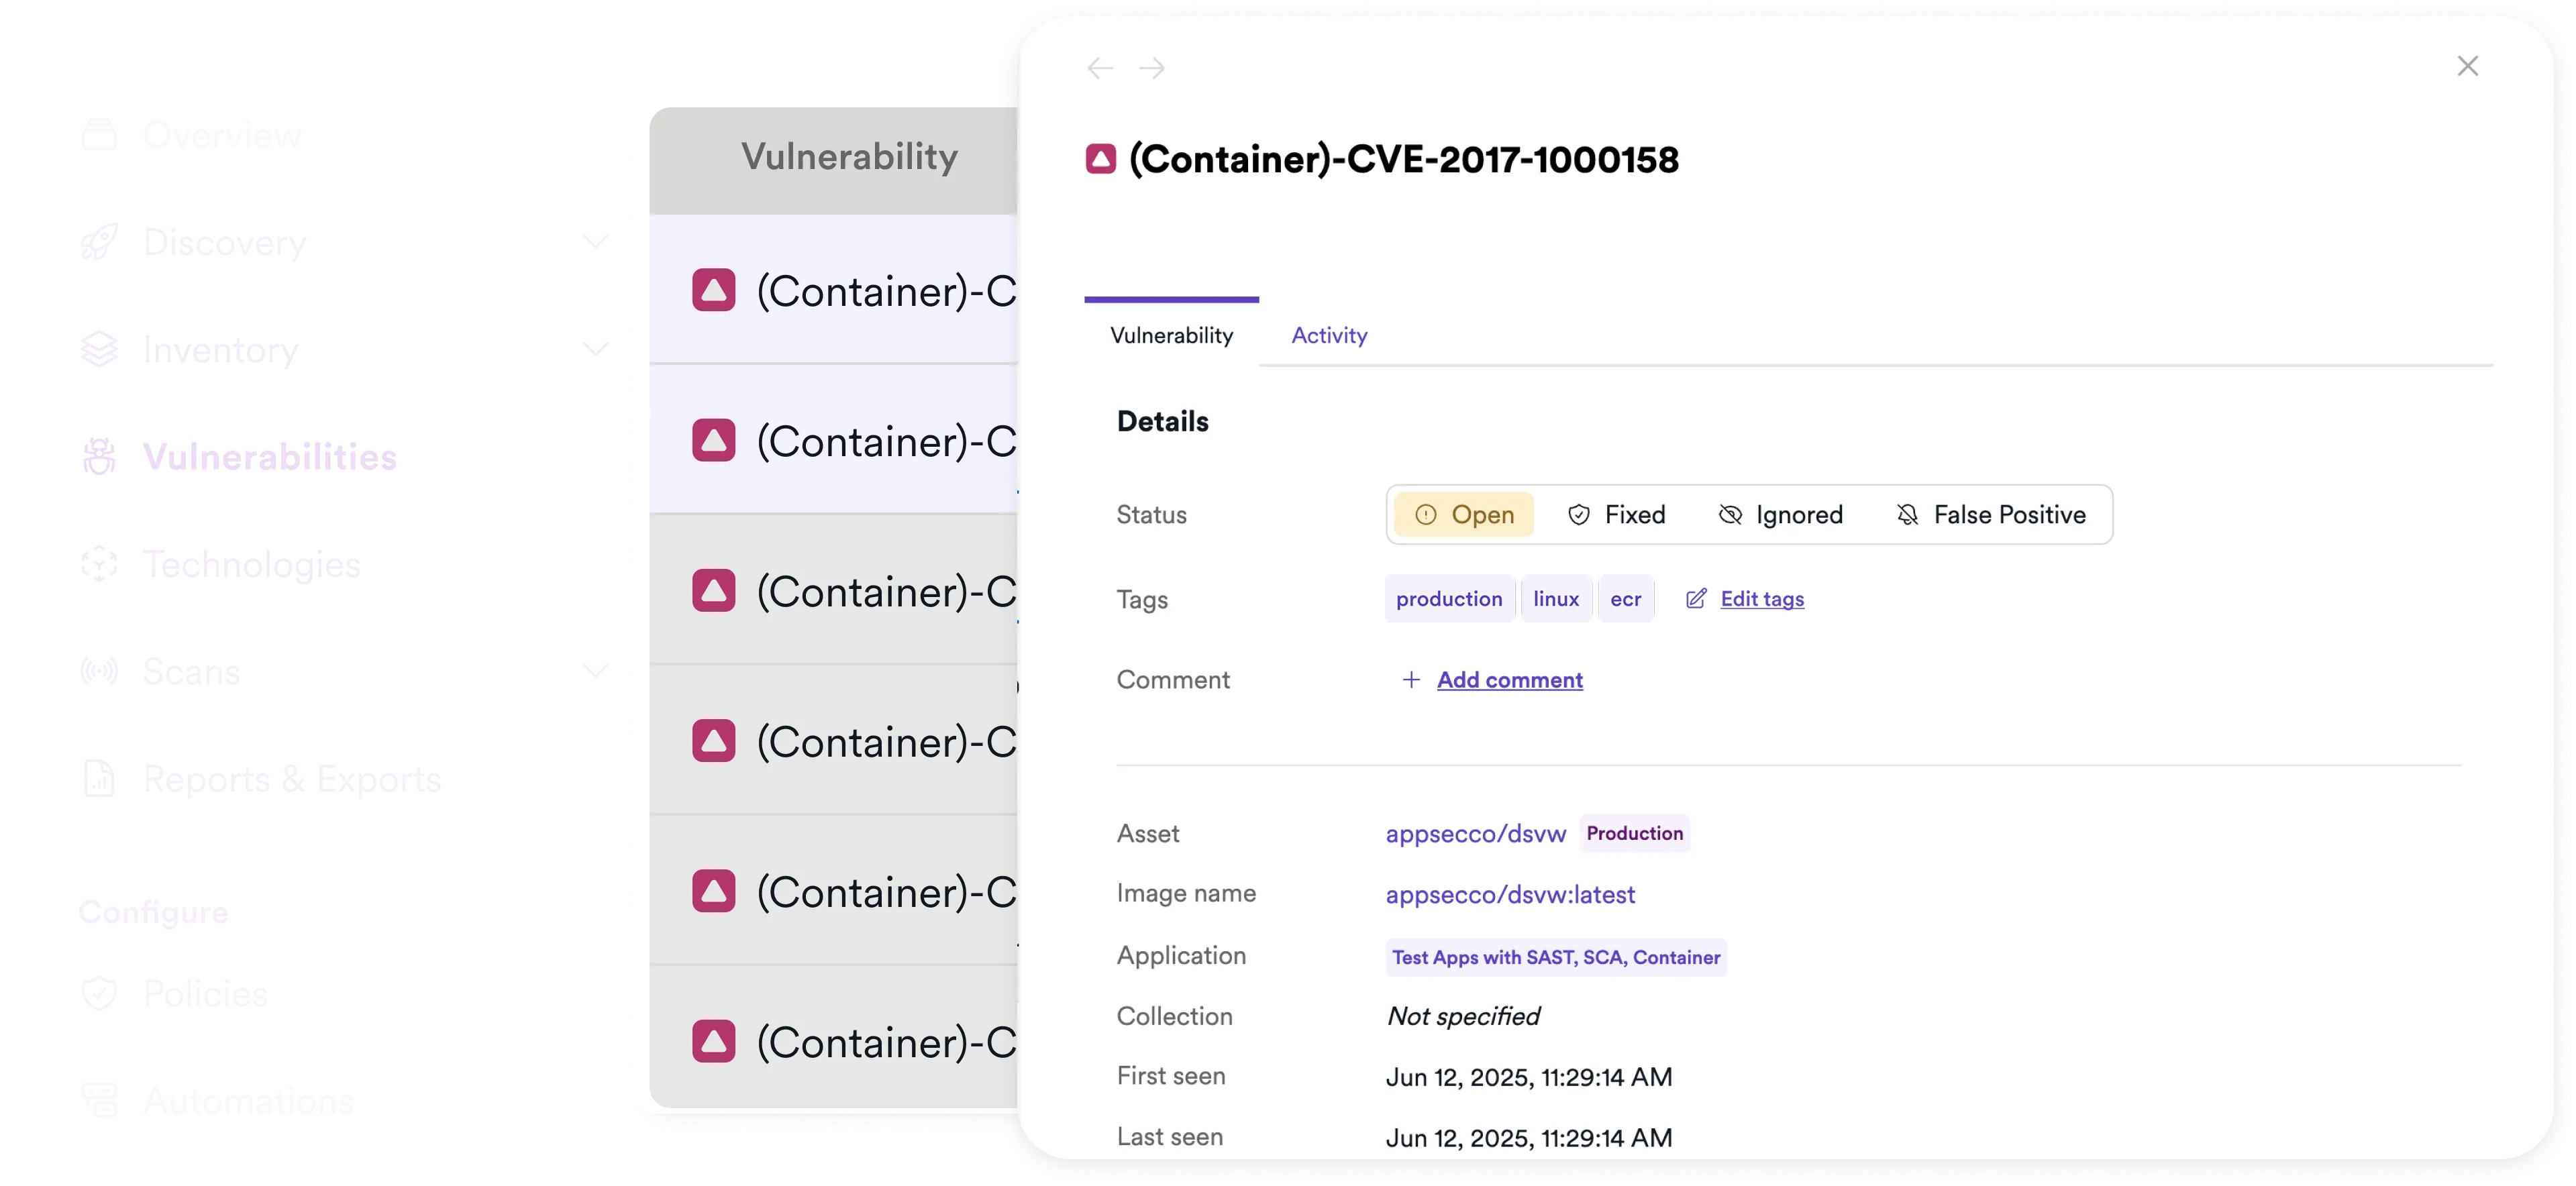
DAST
The industry’s first. Still the best.
Invicti’s industry-leading DAST engine delivers proof-based scanning with an industry-best 99.98% accuracy. Fully integrated into your SDLC, it scales effortlessly across teams and portfolios.
Get a demo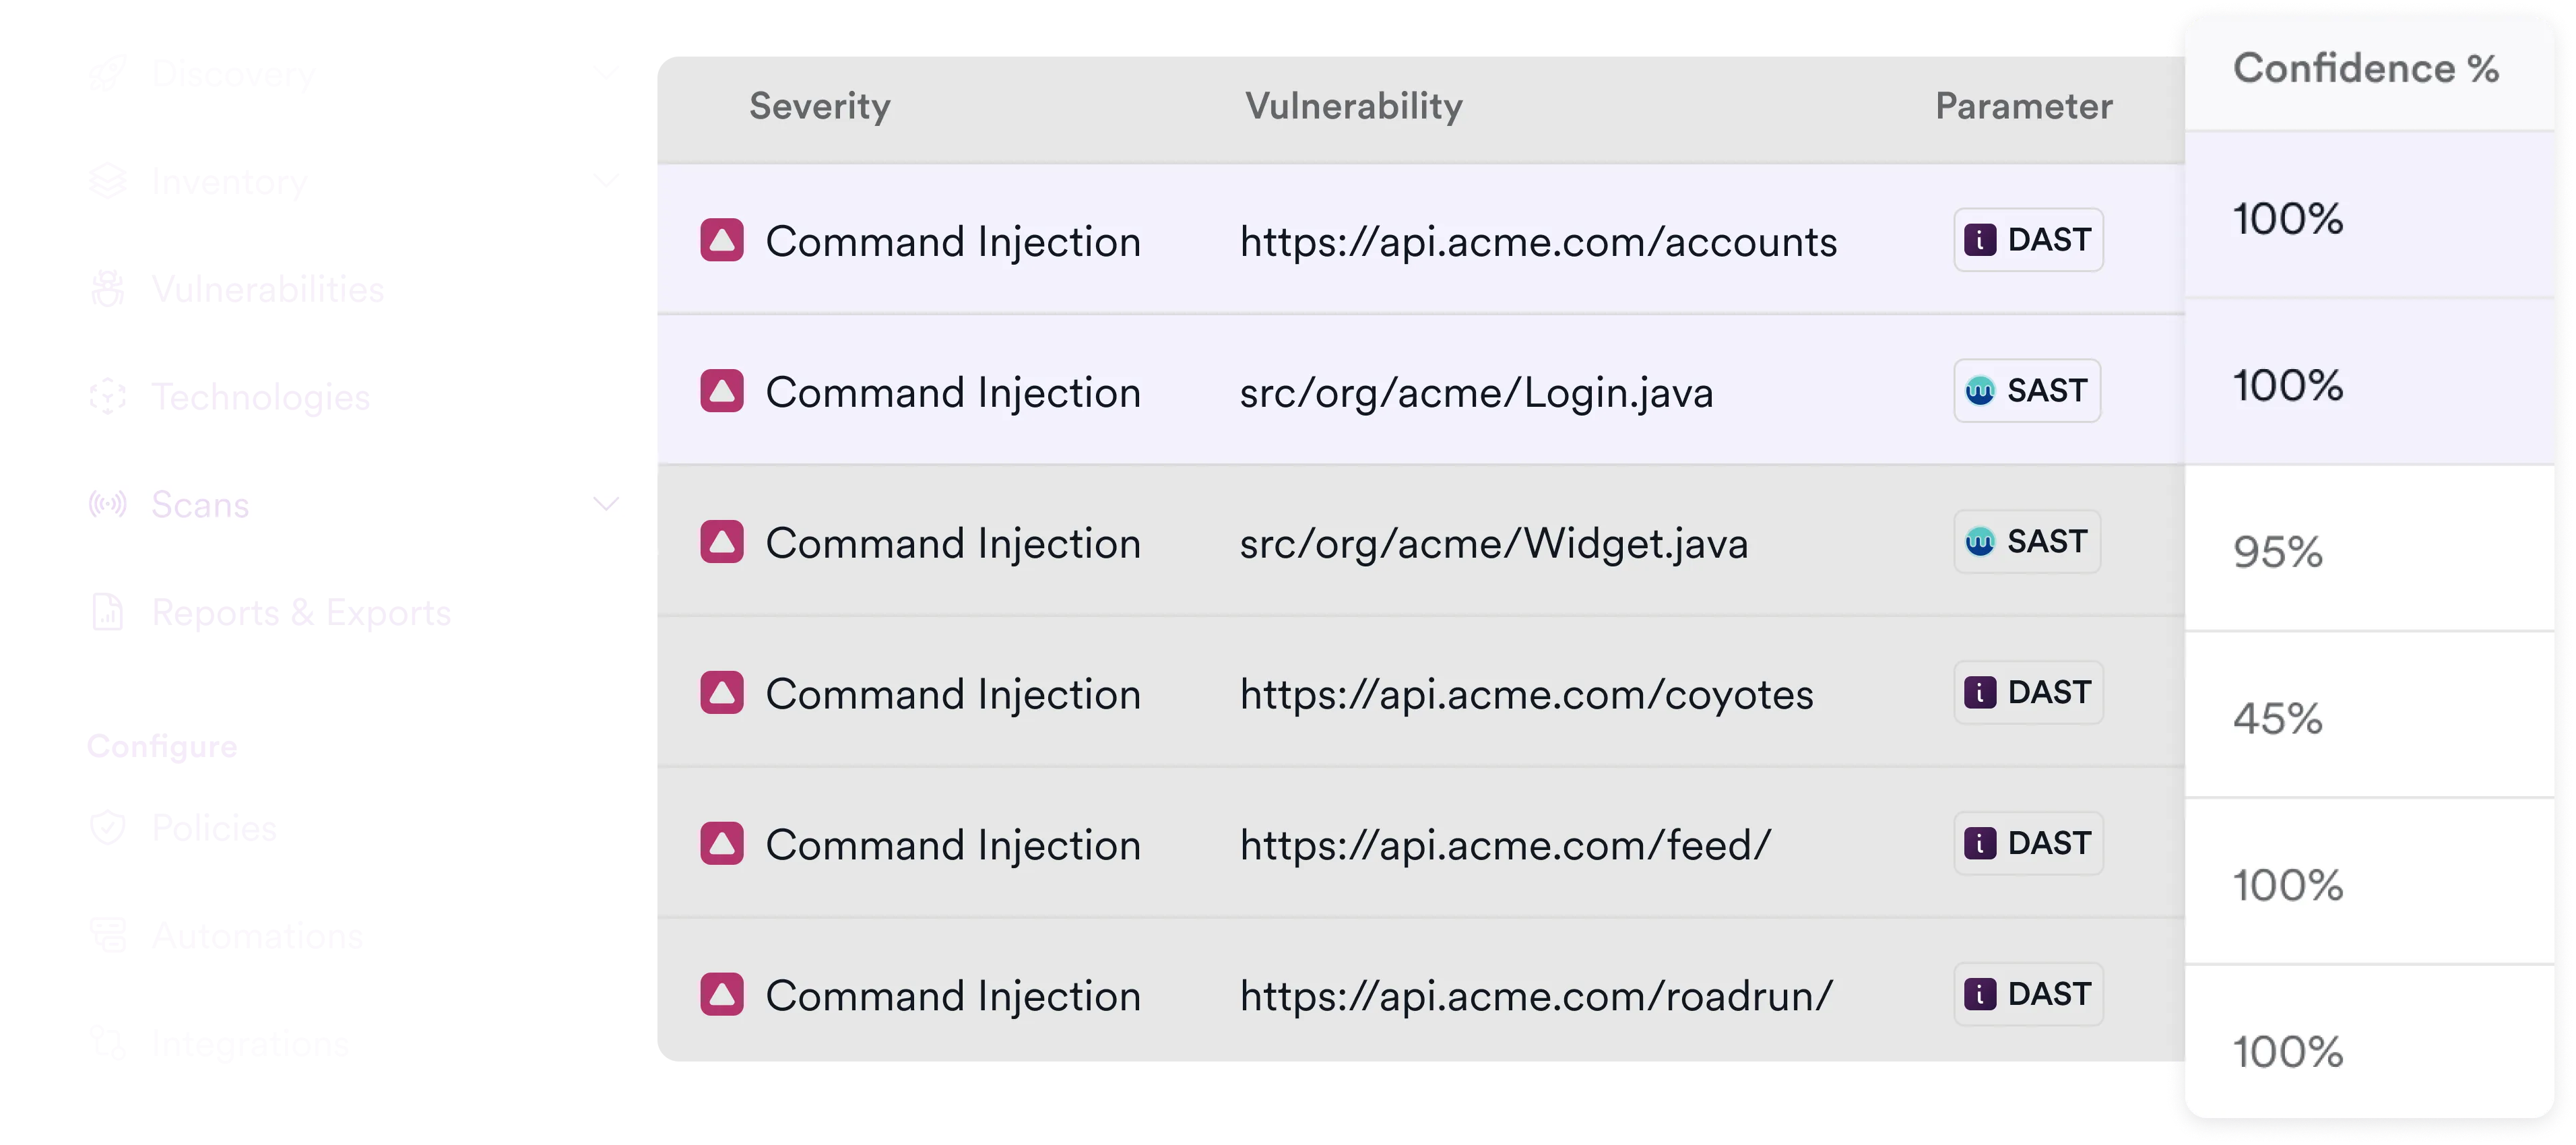
API Security
Discover shadow APIs, reconstruct specs, scan for runtime risks
Invicti scans REST, SOAP, and GraphQL APIs with the same depth and accuracy as web apps—validating vulnerabilities with proof before they reach production. Documented or not, your APIs get full coverage, automatically.
Get a demo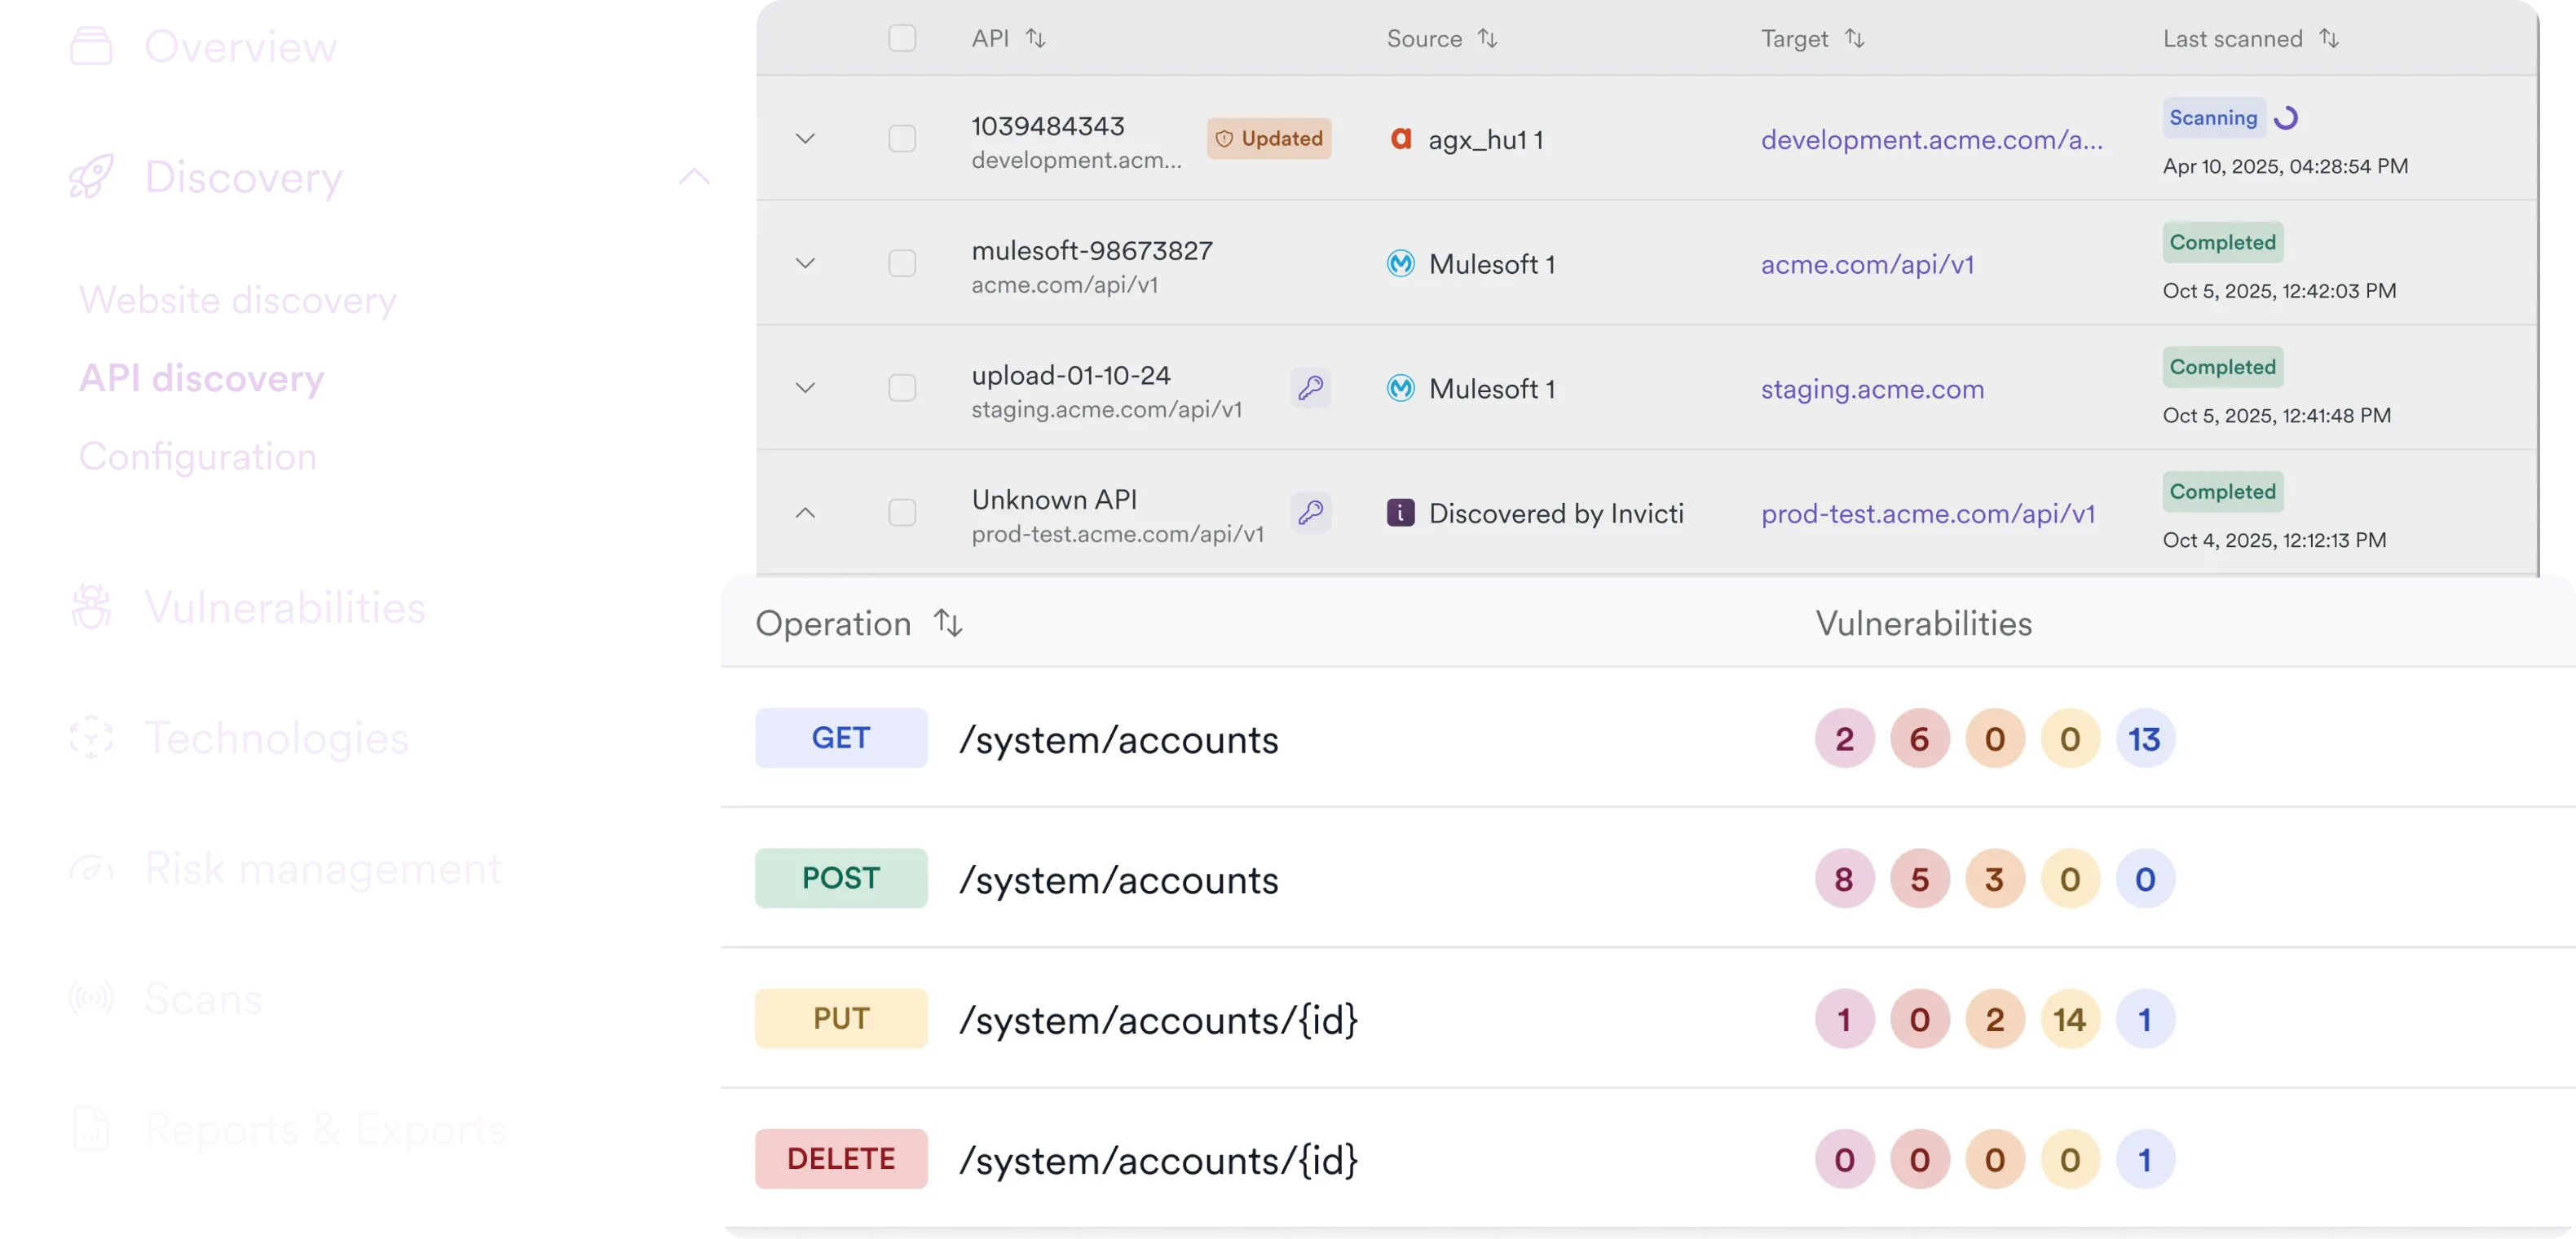
ASPM
Application security posture management (ASPM)
Invicti’s runtime-verified ASPM unifies, validates, prioritizes, and acts on AppSec risk. Get a single source of truth with policy enforcement and audit-ready reporting.
Get a demo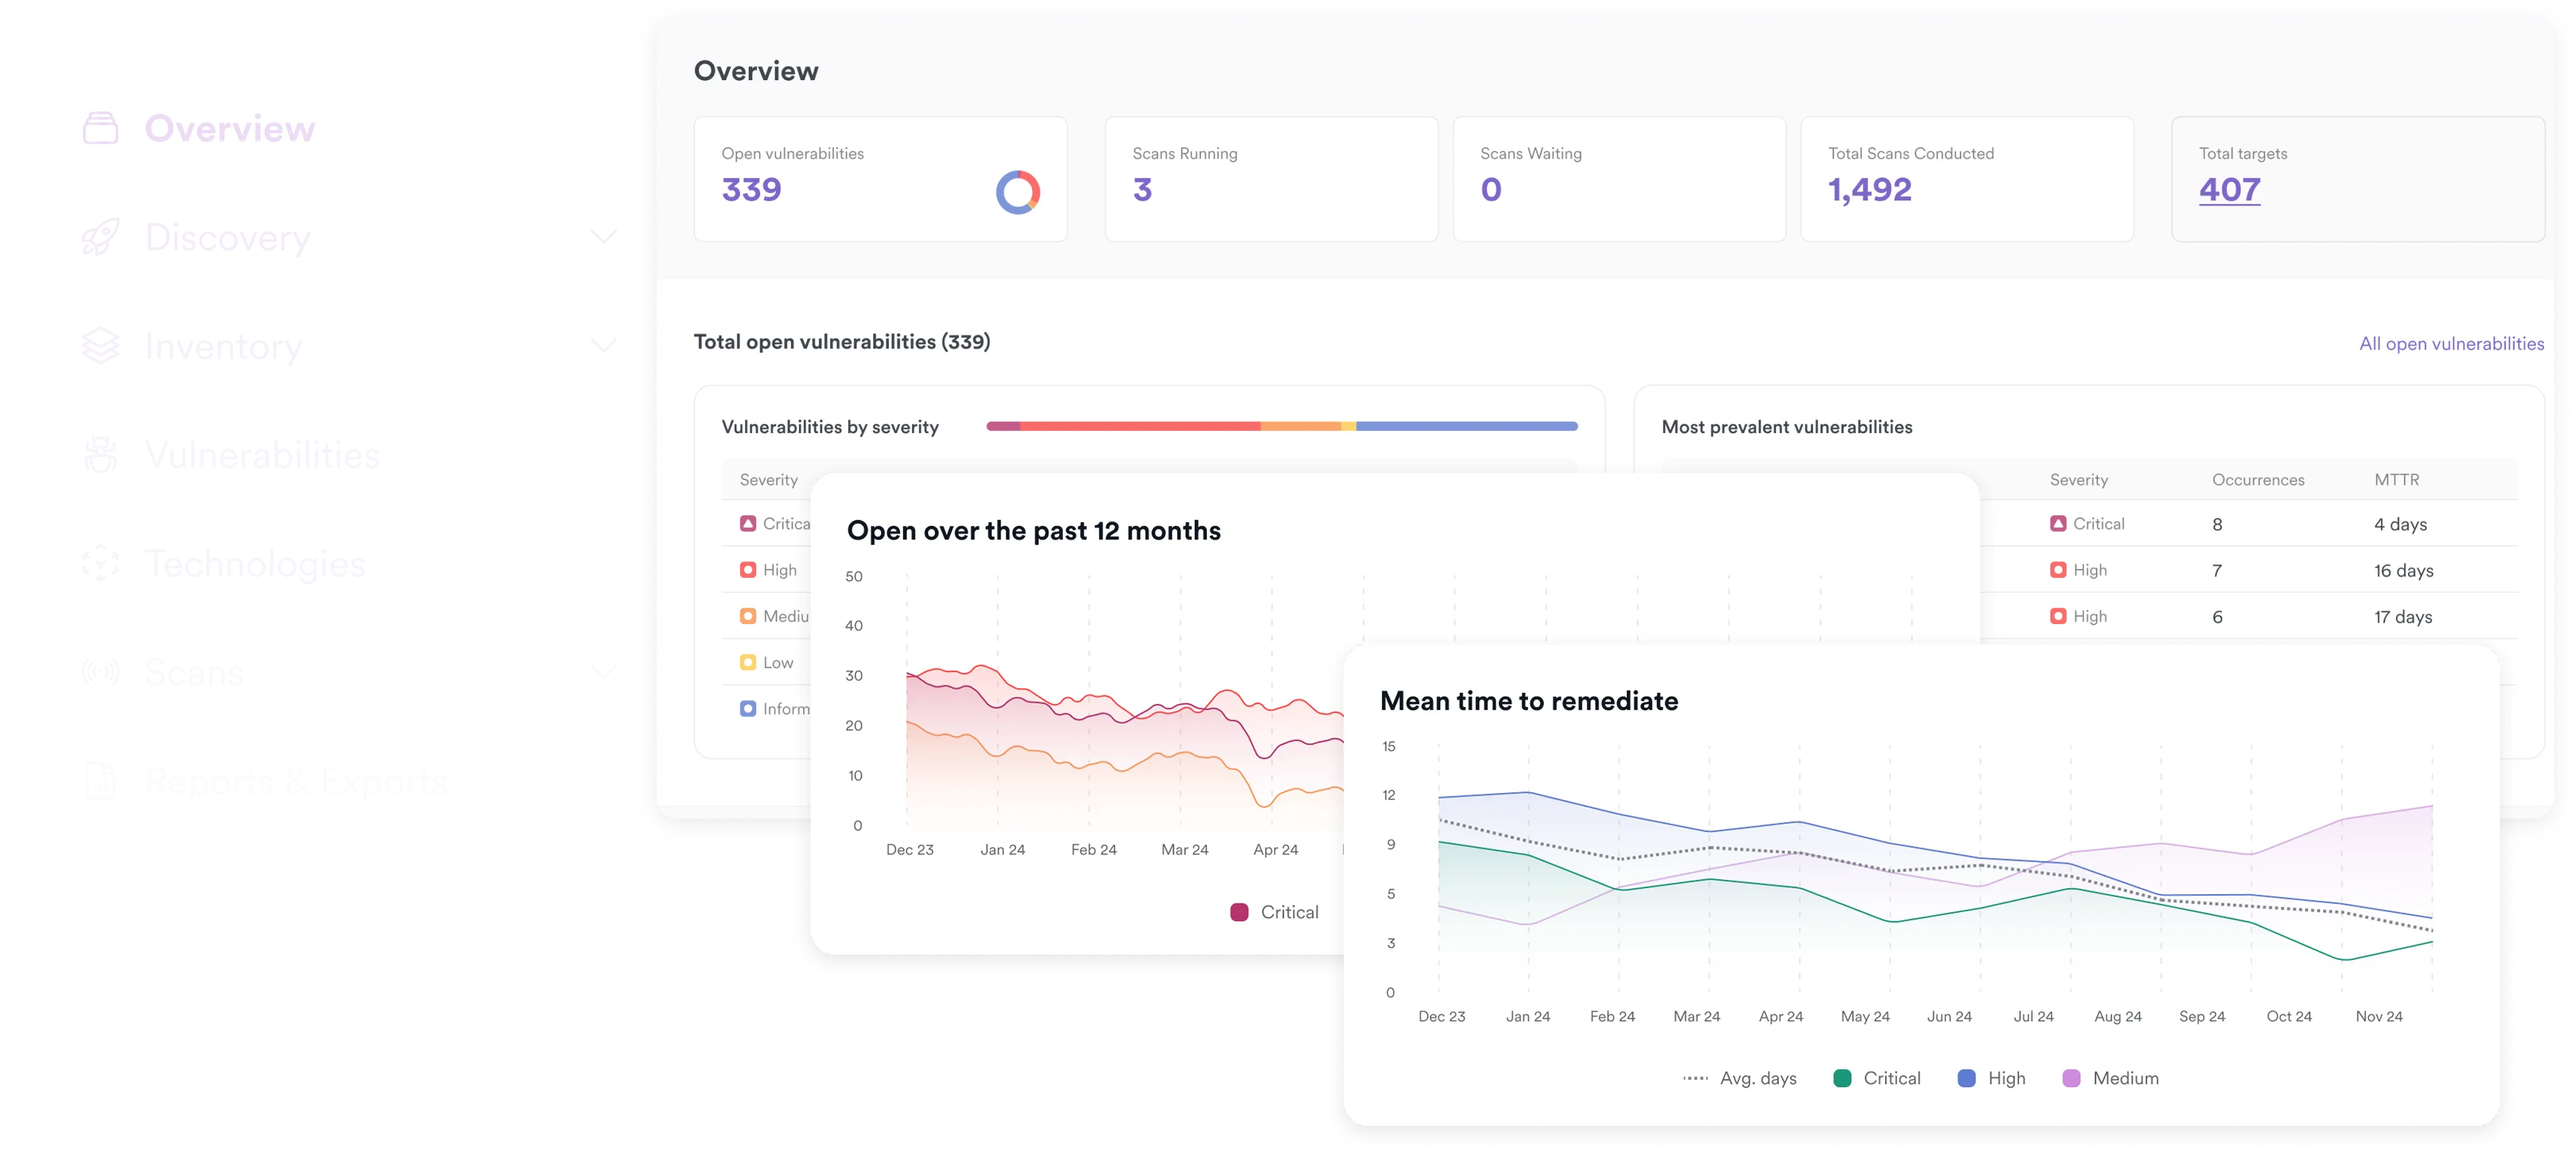
40%
More vulnerabilities found compared to leading competitors
99.98%
Confirmation accuracy for exploitable vulnerabilities
70%
Acceptance rate on AI remediations
Integrations
Seamlessly connect to your existing tools

GitHub Actions
GitHub Actions lets you automate tasks within your software development life cycle.
Asana
Asana is a work management platform designed to help teams organize, track and manage work.
Travis CI
Travis CI is a hosted continuous integration service and used to test and deploy software projects hosted on GitHub.

Azure Pipelines
Azure DevOps is a web-based DevOps manager that provides Azure Pipelines CI/CD pipeline features.

Trello
Trello is a web-based, list-making application for collaboration and project organization.
TeamCity
TeamCity is a build management and CI server that helps run automated tests before production.

Azure Key Vault
Azure Key Vault is a service to store and access secrets. It encrypts keys and small secrets like passwords.

Webhooks
Webhooks provide a way to integrate an issue tracking system that does not have its own integration.

Invicti API
Invicti Team and Enterprise has a full-featured REST API which allows for easy integration.

ServiceNow Application Vulnerability Response
ServiceNow Application Vulnerability Response helps you with tracking, prioritizing, and resolving vulnerabilities.
ServiceNow Vulnerability Response
ServiceNow Vulnerability Response helps you in tracking, prioritizing, and resolving vulnerabilities.

HashiCorp Vault
HashiCorp Vault is a secret management system that provides access to secrets, such as password and API keys, in a secure way.
CyberArk Vault
CyberArk Enterprise Password Vault is a privileged access management system that helps you centrally manage privileged account identities in a single location.
Okta
Okta is an access management platform that secures critical resources by identity controls.

Azure Active Directory
Azure AD is a platform that manages identities with secure SSO and multi-factor authentication.

PingFederate
PingFederate is an enterprise federation server that enables user authentication and single sign-on.
Microsoft ADFS
ADFS provides users with single sign-on access by sharing digital identity and entitlement rights.

SAML
SAML is a security language for exchanging authentication and authorization data between providers.

PingIdentity
PingIdentity is a platform that provides federated identity management and intelligent app access.

ModSecurity
ModSecurity (ModSec) is an open-source WAF that is based on the OWASP ModSecurity Core Rule Set.
Google
Google Single sign-on provides one-click access to pre-integrated apps in the cloud and on-premises.

Imperva SecureSphere
Imperva SecureSphere is cyber security WAF software that protects websites from attacks using custom policies.

F5 BIG-IP
BIG-IP ASM is a WAF that protects your applications from network attacks including OWASP Top 10.
Microsoft Teams
Microsoft Teams is a communication platform that integrates with Office 365 and other products.

Mattermost
Mattermost is an open-source, flexible, messaging platform that enables secure team collaboration.

GitLab CI/CD
GitLab is a web-based repository manager that helps configure source control repositories.
UrbanCode
UrbanCode Deploy automates application developments through your environments.
Jenkins
Jenkins is an automation server that supplies plugins that build automation into projects.
Circle CI
CircleCI is a continuous integration and delivery system used to build multi-platform applications.

Bamboo
Bamboo is an automation server that enables software developers to build automation into projects.

TFS
TFS (Team Foundation Server) is a Microsoft product that covers the entire application lifecycle.

YouTrack
YouTrack is a customizable project management tool that helps you plan and track software workflows.

Shortcut
Shortcut is a project management platform specifically designed for software development.
Splunk
Splunk is a Security Information and Event Management software that reads and stores data.
PagerDuty
PagerDuty is a digital operations management platform that alerts clients to disruption and outages.

Unfuddle
Unfuddle is full-stack software project management software with built in issue tracking tools.

Redmine
Redmine is an issue tracking system that is part of a flexible project management web application.

Pivotal Tracker
Pivotal Tracker is an issue tracking tool to help software development teams in managing projects.
ServiceNow Incident Management
ServiceNow is an issue tracking system that helps organisations to manage issues across departments.

GitHub
GitHub is a web-based hosting service for code version control with an extra issue tracking feature.
Kenna
Kenna is a real-time issue tracking system that specializes in risk-based vulnerability management.
Kafka
Kafka provides a unified, high-throughput, low-latency platform for handling real-time data feeds.

JIRA
Jira is an issue tracking software app with agile project management and bug tracking features.

Jazz Team Server
Jazz Team Server is an issue-tracking system to maintain transparency for the development team.

DefectDojo
DefectDojo is a vulnerability management tool that streamlines the application security testing process.
GitLab
GitLab is an advanced issue tracking tool for planning work and solving problems collaboratively.

Freshservice
Freshservice is an intuitive cloud-based IT help-desk incident and service management system.

Azure Boards
Azure Boards helps teams manage their projects quickly and easily.

FogBugz
FogBugz is a web-based project management system with built in bug and issue tracking features.

Bugzilla
Bugzilla is an open-source, web-based bug tracking and testing tool for managing software defects.

Bitbucket
Bitbucket is a web-based code management hosting service that provides collaboration for teams.

Azure API Management
Azure API Management allows organizations to publish APIs hosted on Azure, on-premises, and in other clouds more securely, reliably, and at scale.

Mend.io
Mend SAST empowers developers to find and fix security vulnerabilities in proprietary code with 10x faster scans, seamless workflow integration, contextual education, and actionable feedback.
Amazon API Gateway
Amazon API Gateway is a fully managed service that allows developers to create, publish, maintain, monitor, and secure APIs at any scale.

Kubernetes
Kubernetes is an open-source container orchestration system for automating software deployment, scaling, and management. Invicti Network Traffic Analyzer integrates with Kubernetes natively and via Istio Service Mesh.

Apigee API hub
Apigee API hub lets you consolidate and organize information about all of the APIs of interest to your organization.

MuleSoft Anypoint Exchange
MuleSoft Anypoint Exchange is a marketplace of reusable, pre-built templates, connectors, accelerators, and APIs from the MuleSoft ecosystem.

Zapier
Zapier is a web-based service that allows users to integrate web apps and automate workflows.

FortiWeb
Fortiweb is a WAF that protects public cloud hosted web applications from threats and attacks.

Cloudflare
Cloudflare is a WAF that examines HTTP requests to websites and applies rules to protect web apps.

Slack
Slack is a team messaging system that enables enterprise teams to communicate via channels.
AWS
Amazon Web Services is a WAF that enables users to monitor, allow and block HTTP and HTTPS requests.
GitHub Actions
GitHub Actions lets you automate tasks within your software development life cycle.
Asana
Asana is a work management platform designed to help teams organize, track and manage work.
Travis CI
Travis CI is a hosted continuous integration service and used to test and deploy software projects hosted on GitHub.
Azure Pipelines
Azure DevOps is a web-based DevOps manager that provides Azure Pipelines CI/CD pipeline features.
Trello
Trello is a web-based, list-making application for collaboration and project organization.
TeamCity
TeamCity is a build management and CI server that helps run automated tests before production.
Azure Key Vault
Azure Key Vault is a service to store and access secrets. It encrypts keys and small secrets like passwords.
Webhooks
Webhooks provide a way to integrate an issue tracking system that does not have its own integration.
Invicti API
Invicti Team and Enterprise has a full-featured REST API which allows for easy integration.
ServiceNow Application Vulnerability Response
ServiceNow Application Vulnerability Response helps you with tracking, prioritizing, and resolving vulnerabilities.
ServiceNow Vulnerability Response
ServiceNow Vulnerability Response helps you in tracking, prioritizing, and resolving vulnerabilities.
HashiCorp Vault
HashiCorp Vault is a secret management system that provides access to secrets, such as password and API keys, in a secure way.
CyberArk Vault
CyberArk Enterprise Password Vault is a privileged access management system that helps you centrally manage privileged account identities in a single location.
Okta
Okta is an access management platform that secures critical resources by identity controls.
Azure Active Directory
Azure AD is a platform that manages identities with secure SSO and multi-factor authentication.
PingFederate
PingFederate is an enterprise federation server that enables user authentication and single sign-on.
Microsoft ADFS
ADFS provides users with single sign-on access by sharing digital identity and entitlement rights.
SAML
SAML is a security language for exchanging authentication and authorization data between providers.
PingIdentity
PingIdentity is a platform that provides federated identity management and intelligent app access.
ModSecurity
ModSecurity (ModSec) is an open-source WAF that is based on the OWASP ModSecurity Core Rule Set.
Google
Google Single sign-on provides one-click access to pre-integrated apps in the cloud and on-premises.
Imperva SecureSphere
Imperva SecureSphere is cyber security WAF software that protects websites from attacks using custom policies.
F5 BIG-IP
BIG-IP ASM is a WAF that protects your applications from network attacks including OWASP Top 10.
Microsoft Teams
Microsoft Teams is a communication platform that integrates with Office 365 and other products.
Mattermost
Mattermost is an open-source, flexible, messaging platform that enables secure team collaboration.
GitLab CI/CD
GitLab is a web-based repository manager that helps configure source control repositories.
UrbanCode
UrbanCode Deploy automates application developments through your environments.
Jenkins
Jenkins is an automation server that supplies plugins that build automation into projects.
Circle CI
CircleCI is a continuous integration and delivery system used to build multi-platform applications.
Bamboo
Bamboo is an automation server that enables software developers to build automation into projects.
TFS
TFS (Team Foundation Server) is a Microsoft product that covers the entire application lifecycle.
YouTrack
YouTrack is a customizable project management tool that helps you plan and track software workflows.
Shortcut
Shortcut is a project management platform specifically designed for software development.
Splunk
Splunk is a Security Information and Event Management software that reads and stores data.
PagerDuty
PagerDuty is a digital operations management platform that alerts clients to disruption and outages.
Unfuddle
Unfuddle is full-stack software project management software with built in issue tracking tools.
Redmine
Redmine is an issue tracking system that is part of a flexible project management web application.
Pivotal Tracker
Pivotal Tracker is an issue tracking tool to help software development teams in managing projects.
ServiceNow Incident Management
ServiceNow is an issue tracking system that helps organisations to manage issues across departments.
GitHub
GitHub is a web-based hosting service for code version control with an extra issue tracking feature.
Kenna
Kenna is a real-time issue tracking system that specializes in risk-based vulnerability management.
Kafka
Kafka provides a unified, high-throughput, low-latency platform for handling real-time data feeds.
JIRA
Jira is an issue tracking software app with agile project management and bug tracking features.
Jazz Team Server
Jazz Team Server is an issue-tracking system to maintain transparency for the development team.
DefectDojo
DefectDojo is a vulnerability management tool that streamlines the application security testing process.
GitLab
GitLab is an advanced issue tracking tool for planning work and solving problems collaboratively.
Freshservice
Freshservice is an intuitive cloud-based IT help-desk incident and service management system.
Azure Boards
Azure Boards helps teams manage their projects quickly and easily.
FogBugz
FogBugz is a web-based project management system with built in bug and issue tracking features.
Bugzilla
Bugzilla is an open-source, web-based bug tracking and testing tool for managing software defects.
Bitbucket
Bitbucket is a web-based code management hosting service that provides collaboration for teams.
Azure API Management
Azure API Management allows organizations to publish APIs hosted on Azure, on-premises, and in other clouds more securely, reliably, and at scale.
Mend.io
Mend SAST empowers developers to find and fix security vulnerabilities in proprietary code with 10x faster scans, seamless workflow integration, contextual education, and actionable feedback.
Amazon API Gateway
Amazon API Gateway is a fully managed service that allows developers to create, publish, maintain, monitor, and secure APIs at any scale.
Kubernetes
Kubernetes is an open-source container orchestration system for automating software deployment, scaling, and management. Invicti Network Traffic Analyzer integrates with Kubernetes natively and via Istio Service Mesh.
Apigee API hub
Apigee API hub lets you consolidate and organize information about all of the APIs of interest to your organization.
MuleSoft Anypoint Exchange
MuleSoft Anypoint Exchange is a marketplace of reusable, pre-built templates, connectors, accelerators, and APIs from the MuleSoft ecosystem.
What customers say
“For more websites, we now don’t need to go externally for security testing. We can fire up Invicti, run the tests as often as we like, view the scan results, and mitigate to our hearts’ content. As a result, the budget we were spending every year on penetration testing decreased by approximately 60% almost immediately and went down even more the following year, to about 20% of our initial spending.”
“Invicti detected web vulnerabilities that other solutions did not. It is easy to use and set up...”
“I had the opportunity to compare expertise reports with Invicti ones. Invicti was better, finding more breaches.”
“Invicti is the best Web Application Security Scanner in terms of price-benefit balance. It is a very stable software, faster than the previous tool we were using and it is relatively free of false positives, which is exactly what we were looking for.”
Learn how we help across industries
Read more case studies ↗FAQs about the Invicti AppSec platform
What makes the Invicti Platform different from other application security tools?
The Invicti Platform takes a DAST-first approach to application security, focusing on exploitable vulnerabilities in live applications rather than theoretical risks. Unlike static testing tools that generate excessive false positives, Invicti uses proof-based scanning to automatically validate vulnerabilities with proof-of-exploit, eliminating guesswork and wasted effort.
How does Invicti help reduce false positives in vulnerability scanning?
False positives are one of the biggest challenges in application security. For many common vulnerability classes, Invicti addresses this with proof-based scanning, which automatically verifies whether a vulnerability is truly exploitable. This reduces alert fatigue and ensures development teams only spend time fixing real, high-risk issues.
What is ASPM and how does Invicti support it?
Application security posture management (ASPM) provides centralized visibility and risk management across security tools, workflows, and teams. Invicti delivers the industry’s first proof-based ASPM by combining its leading DAST and API security with orchestration and management capabilities. This enables enterprises to prioritize, track, and remediate vulnerabilities across all applications with zero noise.
Does the Invicti Platform support API security testing?
Yes. Invicti goes beyond web application scanning to include automated API discovery and testing. This helps organizations cover hidden parts of their attack surface, ensuring both web applications and APIs are continuously identified and secured against real-world threats.
Can Invicti integrate into DevSecOps workflows?
Absolutely. The Invicti Platform is built for automation and scalability, with integrations into CI/CD pipelines, issue trackers, and collaboration tools. This allows security testing to run continuously in DevSecOps environments without slowing down development, ensuring vulnerabilities are detected and remediated early.
Does the Invicti Platform cover supply chain risks such as open-source components and containers?
Yes. The Invicti Platform includes software composition analysis (SCA) and container security capabilities, allowing organizations to identify vulnerable open-source libraries, outdated technologies, and insecure container images. Combined with dynamic testing, this provides both static and runtime visibility into supply chain risks for a more complete security posture.
Built for modern AppSec
From discovery to remediation, manage every application risk in one place.
Get a demo- 99.98% accurate scans: slash manual triage
- Scalable deployment: govern 1,000+ apps
- Seamless integration: security in your SDLC
- Built to prevent false positives: confidence in results